


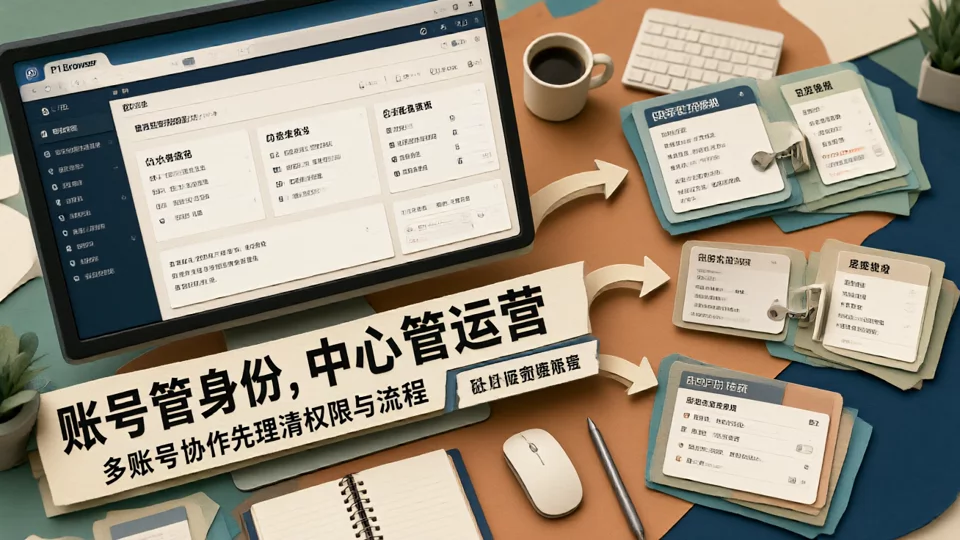
At nine AM, an operator logs into Amazon Seller Central to reply to buyer messages; at noon, they switch to the ERP to batch-adjust prices for two sites; and in the afternoon, they synchronize inventory for a third store. Each store operates normally when handled individually. However, once these actions are consolidated, CAPTCHAs start popping up frequently, inventory gets written to the wrong store, and the account permissions of a colleague who left the company last month remain active in the backend.
These issues rarely stem from the tools themselves. More commonly, they result from a lack of fixed correspondence across four layers: who the account entity is, what role is assigned in Seller Central, which environment is used for login, and which scopes the tool is authorized to write to. Below, following the order of these four layers, we first clarify the division of labor between Amazon seller accounts and Seller Central, then discuss the connection sequence for store management tools, and finally provide attribution for common failures and a pre-implementation self-check method for tools.
Clarifying the Distinction: The Seller Account is Identity, Seller Central is the Workspace
The Amazon seller account resolves "who you are": the registered entity, business license and legal representative information, payment accounts, tax information, and verification materials all reside at this layer. It determines whether the account is compliant on the platform, whether it can receive payments, and whether it can pass audits, making it an identity asset where a single change impacts the entire system.
Seller Central, on the other hand, is "where you work": orders, inventory, pricing, advertising, buyer messages, performance metrics, and reports are all managed here, where sub-accounts and role permissions are also allocated. Issues at the identity layer manifest as account audits or suspensions, while issues at the operational layer manifest as incorrect price changes, misshipped goods, or former employees retaining login access. The troubleshooting paths for these two are entirely different; conflating them often leads to misidentifying permission issues as account issues.
The Boundary of Amazon Seller Accounts: One Account Per Region, with Business Rationale for Multiple Accounts
The official stance of Amazon in seller announcements is: typically operate one account per region; multiple accounts are permissible when there is a reasonable business need; accounts should be maintained in good standing, as policy issues with one account may affect related accounts (seeMulti-Seller Account Guidelines on the Amazon Seller Forum).
This principle dictates the order of operations: first confirm whether there are legitimate business reasons for multiple accounts, then discuss how to manage them with tools. Reversing this order—buying a multi-store management tool before providing compliance explanations at the account level—places the risk upfront. Additionally, one must accept the reality that platforms may reference various signals, such as registration details, payment information, login environments, and operational behaviors, to determine if accounts are associated. Specific criteria are subject to account notifications and official policies; simply switching browsers or networks does not serve as a reliable conclusion.
Four-Layer Mapping: Account Entity, Seller Central Role, Login Environment, Tool Write Scope
Drilling down into the previous two layers yields a reusable cross-reference table: the account entity defines identity and compliance boundaries; the Seller Central role determines what each user can see and operate in the backend; the login environment determines where the operation is initiated; and the tool write scope determines which fields third-party systems are permitted to modify. There must be a fixed correspondence between these four layers—operations for a specific store must be performed by the assigned sub-account, within a specified environment, and only writing to stores within the authorized scope.
If this correspondence loosens, issues will manifest as 'the tools are not user-friendly.' In practice, mapping out these four layers first and then adding people and tools is far more efficient than selecting tools first and patching up the processes later.
How to slice roles in Seller Central: Assign by job function, do not share the main account
The goal of role segmentation is not to divide permissions into the smallest possible pieces, but to ensure that each person's permission scope aligns with their job responsibilities and can be cleanly revoked during personnel changes. Refer to the following division logic:
- Main AccountRetain exclusively by the account owner for permission allocation, changes to payment and tax information, and account-level appeals. Do not use for daily operations.
- OperationsGain access to product information, pricing, inventory, and order processing, typically restricted to the specific sites or categories you manage.
- Customer SupportRequires only buyer messaging and return/exchange handling permissions; it should not have the ability to modify prices or write to inventory.
- FinanceFocuses on settlement reports, expense details, and reconciliation exports; read-only access is generally sufficient.
- AdvertisingGrant separate authorization for the advertising backend and budget adjustments, keeping it distinct from product editing permissions.
Reassignments and offboarding are the real test of this division of labor: permission revocation must follow a fixed process with a designated responsible party, rather than manually scrubbing the backend after someone has already left. A more comprehensive breakdown of this structure can be found inMulti-account operations checklist for Amazon Seller accounts and Seller CentralThis is not repeated here.
How to connect store management tools: scope first, then bulk operations; read-only access first, then write access
The most common mistake when integrating tools is enabling all stores, modules, and permissions at once and expecting it to run correctly on day one. A more stable approach is to open things up layer by layer:
- List the modules firstClearly identify which functions this tool needs read/write access to among orders, inventory, pricing, customer service, and advertising. A tool used only for order printing does not need price write permissions; excessive permissions are bound to be misused eventually.
- Then verify account mappingEnsure that each store connection established in the tool corresponds to a specific sub-account or authorization relationship in the seller center, avoiding a mismatch where the tool has permissions but no corresponding role can be found in the backend.
- Start with read-only mode first:Actions like pulling orders and syncing reports, which do not modify backend data, should be executed first to verify that store ownership, currency, and timezone settings are correct.
- Low-traffic write tests on a single store:First, test price adjustments and inventory synchronization on a single store with a small number of SKUs, manually verifying that the backend results match the tool's display.
- Then enable bulk operations:Only after confirming that single-store writes are accurate should high-impact actions such as bulk price changes and cross-store inventory synchronization be enabled, while maintaining operation logs and rollback capabilities.
During the selection phase, it is also necessary to distinguish the capability boundaries of tools: ERP systems focus on centralized processing of orders and inventory, while browser-based tools focus on isolation of login environments; the two do not solve the same problem. Specific comparison dimensions can be found atSelecting Tools for Amazon Seller Central and Multi-Account Operations; If your team is just starting out and is still comparing general-purpose ERPs,Comparing Dianxiaomi and Mangguo Shop Manager: A Decision Checklist for BeginnersIt outlines a decision path based on platform focus, store structure, and team size.
Common Fault Attribution: Which Layer Causes Frequent CAPTCHAs, Writing to the Wrong Store, or Residual Permissions?
Frequent CAPTCHA Pop-upsThis is mostly related to the login environment layer—logging into the same account from multiple environments within a short period, or multiple people sharing the same login identity. First, check whether someone is sharing the main account, then check if the environment is being switched randomly.
Inventory and Prices Written to the Wrong StoreThe issue lies in the tool's writing layer. This usually happens when store authorization is not mapped one-to-one, or when the selection range is too broad during batch operations. First, reproduce it on a single store and single SKU to verify the mapping relationship before resuming batch processing.
Permissions of Departed Employees Are Still ActiveThe issue lies in the role layer. Seller Central sub-accounts and tool sub-accounts are two separate sets of authorizations. Deleting only one leaves the other still active.
A Self-Check Before Integrating Store Management Tools: Define Permissions First or Deploy the Tool First?
The answer depends on your current stage, not the tool's feature list. If a single store is running smoothly and you are preparing to open a second one, define the entity and roles first, then choose the tool; if you already have five or six stores distributed among different people, start with a permissions audit before discussing centralized management. The basis for judgment is simple: if the same problem recurs across different stores, it indicates a gap at the process level that will not disappear by switching tools.
Before integrating new stores into the same system, cross-check account entities, seller center roles, login environments, and tool write scopes using a four-layer mapping; confirm that each item has a clear owner before enabling batch write permissions.
FAQ
Are sub-accounts in the seller center and sub-accounts in the ERP the same set of permissions?
No. Seller center sub-accounts are platform-side authorizations that determine whether a person can access the backend and which modules they can operate; ERP sub-accounts are tool-side accounts that determine which stores they can see and which actions they can execute in this system. They must be configured and revoked separately; changing only one side is equivalent to not changing anything.
What are the practical issues with the team sharing the main account password?
Besides being unable to trace who changed the price or inventory, it also makes the login environment layer uncontrollable: the same person logging in with the same identity from different locations and devices easily triggers additional identity verification. Keeping the main account with the person in charge while operations use their own sub-accounts is a more efficient approach.
Does multi-account operations necessarily rely on browser isolation tools?
Not necessarily, it depends on the number of stores and team size. When there are few stores and a single type of personnel, fixing sub-accounts and login environments is sufficient; when there are many stores and multiple people collaborating, environment management becomes an independent requirement. Tools solve the order of the environment layer, but they cannot replace the compliance judgment at the account entity layer.
For a new site, should you apply for an account first or configure the tool first?
First, apply and pass account verification, and confirm that your payment and tax information are valid before considering connecting your new store to your existing tools. Integrating write-based tools at a stage when the account is still unstable can complicate troubleshooting, as any issues with verification or information changes will involve both the platform and the tools.

