


Logging into three TikTok Shop stores individually works fine. After one operator begins centrally handling messages, updating prices, and syncing inventory, verification codes start popping up frequently, orders are sent to a different store, and an employee who left two months ago still has their account left in the tool. This scenario is common in teams of 1–20 people, but it is usually not an issue of “insufficient tool functionality.”
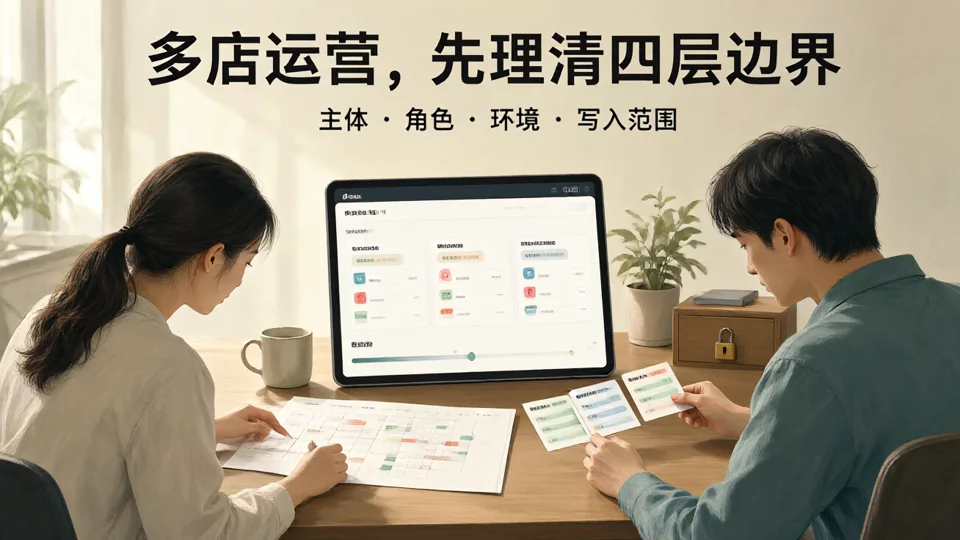
What is truly broken is the mapping between four things: account entities, Seller Center roles, login environments, and tool write scopes. Store management tools can reduce manual switching and unauthorized operations, but they cannot define these four layers of boundaries for you—boundaries must be established before onboarding.
Why issues arise after moving from single-store normalcy to centralized multi-store operations
In the single-store phase, one person, one set of credentials, and one computer keep all the context in their head. When expanding to the second and third stores, teams typically do three things at the same time: connect all stores to the same ERP, let operators share one login method, and grant full permissions first to make testing “convenient.” Each step seems reasonable on its own, but combined, they disrupt the originally clear mappings.
The symptoms after the disruption follow a pattern: increased verification codes are often linked to the login environment bouncing back and forth across multiple stores; orders going to the wrong store are usually due to store entries in the tool not being locked to account entities; and lingering permissions from departed staff occur because permissions are attached to individuals rather than job roles. None of these are functional defects, and tightening configurations may not immediately make them disappear; the platform's specific judgment logic is not fully public, so one should rely on account notifications and official policies.
First, distinguish between TikTok Shop seller accounts, Seller Center, and store matrices
These three terms are often used interchangeably, but their boundaries determine what tools can and cannot do.
Account subjectis the operating entity that bears responsibility: who owns the business license, legal representative, settlement and tax information, and contact details.Seller Centeris the backend interface that this subject sees after logging in; store managers, customer service, and finance each handle their respective tasks within it.Store Matrixrefers to a group of stores that may share certain qualifications but should not share operational credentials.
In the tool, “multi-store” should be represented as multiple independent store entries, each bound to a specific account entity and login environment, rather than a “super entry” that allows free identity switching. Once the tool builds multi-store as the latter, you will not be able to answer “who issued this price change, and in which environment?” when problems occur. For structuring the account framework, you can refer to Introduction to TikTok Shop Seller Accounts and Operations Tools for the distinction between seller center roles and store matrices.
Correlation risks are not single-factor: four corresponding layers must be established first
- Account Entity Layer: Which business entity, which set of qualifications, and which receiving account correspond to each store must be documented in a cross-reference table. Multi-stores under the same entity are handled differently from multi-stores across different entities.
- Seller Center Role LayerStore managers, operations, customer service, and finance each have distinct roles and module access levels within the Seller Center. Clearly define responsibilities by position before moving to tools. Sharing a primary account is the most common breach point at this layer.
- Login Environment LayerThe specific positions, devices, and network environments used to manage which stores need to be fixed and logged. Frequently switching between multiple stores within the same environment is a common source of verification code errors and anomaly alerts, but it is not the only factor.
- Tool Write LayerDefine what ERP or store management tools can modify—read-only orders, price changes, message sending, or inventory adjustments. Granularity should be set by store and position, not by granting a single "full-permission sub-account."
Beyond the four layers, two easily overlooked boundaries are the consistency of data and payment information (whether the address, phone number, and payment details of the same entity on the platform are consistent) and the operational behavior itself (bulk price changes, high-volume new listings in a short period, logins during abnormal hours). There are no public, complete rules on whether platforms consider these risk signals and how they handle them; what teams can do is ensure traceability at each layer.
Distributing permissions by position and avoiding shared login credentials are principles repeatedly emphasized by platforms. TikTok in Business Center Role and Permission Descriptionsrequires assigning access scopes matching assets to member positions and explicitly states not to share login credentials. It should be noted that the Business Center is the backend for advertising and business assets, and it is not the same system as the TikTok Shop Seller Center, but the principle of "granting permissions by position and not sharing credentials" applies to both.
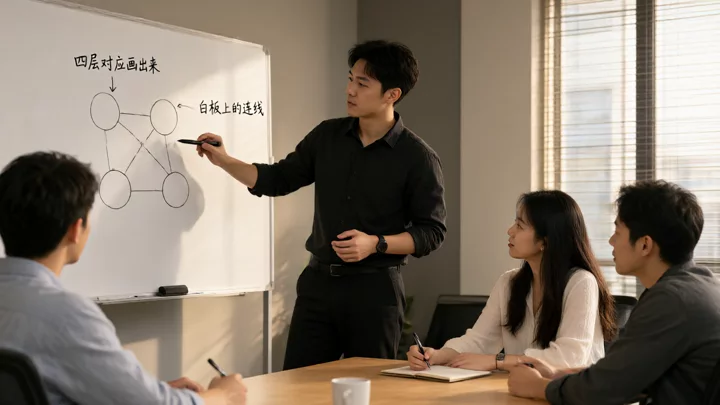
Store management tool onboarding sequence: start with the entity, then roles, then the environment, and finally data writing.
If the order is wrong, every subsequent step will require rework. Proceed in the order below; each step produces a verifiable deliverable.
- Confirm store ownership and the account entity.List the entity, qualifications, payout account, and current admin for each store to build a cross-reference table. Do not onboard stores with unclear ownership or mismatched qualifications.
- Split seller-center roles by job function.Customer support does not need the finance module, and operations does not need to modify settlement details. Split roles in the seller center first before discussing the tool side.
- Pin down the login environment.Clearly specify which role operates on which device over which network to manage which store. Document this in your operational guidelines rather than relying on verbal agreements or ad-hoc instructions in group chats.
- Grant the minimum necessary write access.Start with read-only access to orders and message replies only. Enable write permissions for pricing, inventory, and settlements on a per-store basis, and expand access gradually after a period of observation.
Pause integration in the following scenarios: the legal entity does not match the required qualifications; the store is currently under platform review or performance warning; multiple users share a primary account that cannot be split in the short term; or the tool cannot enforce write permissions per store. Integrating under these conditions will only scale issues that are currently limited to a single store to all stores.
Pre- and post-integration checklist: Use key signals to determine if operations are under control.
The checklist doesn't need to be large; covering four time points is sufficient. The focus is not on the number of items, but on ensuring that each item can be tied to a specific person and a specific store.
| Time Point | Check Item | Judgment Criteria |
|---|---|---|
| Before Tool Setup | Store—Entity Cross-Reference Table | Each store can be mapped to a unique entity and payment account |
| Before Tool Setup | Seller Center Roles | Each active user has a role corresponding to their job position, with no shared main accounts |
| During Integration | Login Environment Log | Devices, networks, and shops are mapped to one another; changes are audited |
| In onboarding | Tool write scope | Set by shop and role separately, read-only by default |
| Post-launch | Cross-shop errors and captchas | With records and attribution — not just a feeling that things are better lately |
| Staff departure | Recovery chain | The seller center role, tool sub-account, and login environment are retracted in three places simultaneously |
Of these, the “wrong store and verification code” item is the most likely to be overlooked. It is recommended to create a simple ledger to record the time of occurrence, the affected store, the operator, and the environment in use. In two weeks, you will be able to determine whether the issues were caused by environmental factors, mapping errors, or a shortage of personnel rushing to catch up.
When expanding to multi-platform operations such as Amazon and Shopify, which practices cannot be directly reused
TikTok Shop's "multi-store" refers to a store matrix within the platform, Shopify's "multi-site" refers to seller-owned site assets, and Amazon's multi-account setup has clear compliance prerequisites linked to account health. Applying a single permission model to all three will cause issues.
Amazon's official guidance on multiple selling accounts states that typically one account is operated per region, multiple accounts are permitted if there is a reasonable business need, and policy issues with one account may affect related accounts (see Amazon Multi-Selling Account Health Tips). This means on the Amazon side, "multiple accounts" is primarily a compliance judgment rather than a tool configuration issue—before connecting any tool, first confirm that the rationale for the existence of multiple accounts can be clearly articulated.Checklist for Related Account Risks in Amazon Multi-Account Operations to expand on this layer in greater detail.
On the Shopify side, the focus is on site asset ownership and employee permissions, with the official Help Center providing clear explanations regarding store members and permissions (Shopify Official Help Center). When integrating third-party tools, this permission framework should be aligned first rather than blindly copying TikTok Shop's store-to-role mapping; specific differences can be compared against the division of labor between TikTok Shop multi-account operations and Shopify independent site management.
When expanding to AliExpress, Shopee, Lazada, and Temu, the same principles apply: you can reuse the verified integration process, but not the mapping relationships. For each platform, first redo the four-layer correspondence based on its specific account structure, then decide which tools to share and which must be kept separate. For reference on the selection approach, see Multi-Platform Seller Tool Selection and Multi-Account Operation Strategy. If account disposal has already occurred after an integration, follow the instructions in the notification for the handling order. Refer to Appeal and Recovery Process After Account Suspension.
FAQ
Is a four-layer mapping required even with only two TikTok Shop stores?
Yes, but it can be simplified to two lines: one line for the store and entity, plus the receiving account; the other for who operates which store on which device. At the two-store stage, the most common issue is mixing one person, two devices, and two identities. Fix these two lines first, then add roles and write scopes when expanding to a third store. This approach is easier to sustain than implementing the full set from the beginning.
Can store management tools completely avoid account linking when logging into multiple stores on the same computer?
No. What tools can do is ensure each action is traceable to a specific store, role, and environment, reducing accidental operations and credential sharing. Platforms have not fully disclosed how they determine account associations. No tool should promise 'complete avoidance.' If you encounter account warnings, follow the platform notifications and official policies.
How do permissions in Seller Center sub-accounts correspond to ERP sub-accounts?
Use the role as the common baseline rather than creating a one-to-one mapping. First, determine which modules this role can access in the Seller Center, then configure an equivalent or smaller scope in the tool. The principle is that permissions on the tool side must not exceed those on the Seller Center side; otherwise, you may encounter situations where changes cannot be made in the backend but can be made in the tool.
After integrating the ERP, what are the first three signals to check?
The frequency of records written to the wrong store, verification codes and secondary verification, and whether permission changes are logged. All three can be attributed to specific stores and specific individuals, making it easier to determine whether write access should be tightened compared to simply having a “general feeling of stability.”
When expanding from TikTok Shop to Amazon or Shopify, can the original tool be reused directly?
The tool may support multiple platforms, but the mappings cannot be copied as-is. Amazon multi-account setups first require a compliance assessment, while Shopify multi-store setups involve self-owned site assets and a different permission model. Before integration, you should redo the mapping of entities, roles, environments, and writes for the new platform before deciding which processes to reuse.

