


In the morning, you reply to messages for Store A on the same computer, in the afternoon you switch to Store B to change prices, and by the end of the month, Store C's collection account is blocked by risk control—when these three events coincide, many people immediately conclude that they have been flagged for association by the platform. More common causes lie elsewhere: a lack of fixed correspondence among the four layers of store registration entity, collection account, login environment, and employee permissions causes verification codes to appear frequently, orders to be written to the wrong store, permissions of resigned employees to persist, and the source of funds on the collection side to be unclear. These four types of issues emerge simultaneously. If the four layers do not align, changing the IP or browser merely masks one of the layers.
The following discussion covers only stores that sellers have the right to operate themselves and for which the business details are accurate. It proceeds according to “four-layer alignment, payment consistency, post-freeze handling sequence, fixed login environment, and permission segmentation.” It provides documented practices, not a guarantee of being “immune to account freezes.”
When issues arise across multiple stores, check the four-layer alignment first instead of switching tools.
Verification codes, wrong store entries, residual permissions, and payment reviews may look like four separate categories of problems, but they often stem from the same source: a specific layer being shared by multiple people, or the environment being changed ad hoc for every operation, which causes the records in the other three layers to contradict one another. First, clearly list the responsibilities of each of the four layers, common mismatches, and the minimum records that must be kept, then decide whether to change tools. Tools can only carry the alignment relationships; they cannot establish them for you. When verifying item by item, you can refer tothe Amazon multi-account operation related risk checklistand expand the scope of checks to stores on other platforms.
r>| Tier | Scope of Responsibility | Checkpoints | Common Misalignments | Minimum Audit Trail |
|---|---|---|---|---|
| Account Entity | Business license, registration documents, contact person, and tax information | The entity documentation and contact information for each store must be independently verifiable | Multiple stores share the same contact details and return address without any explanatory notes | List of entity documents and the dates of any changes |
| Payout Entity | Account name, account holder, intended use, and reconciliation basis | The store owner and the receiving account owner must be the same entity. For third-party receiving, complete the store authorization as required by the service provider. | Receiving payments for a company store via a personal account; funds from multiple stores are consolidated into a single account. | Screenshots of authorization and monthly transaction statements. |
| Login environment. | Device, network, browser profile, and 2FA holder. | Each store should have a fixed setup, which is registered in the record. | Using the same browser profile to log into multiple stores alternately; 2FA is linked to a former colleague's phone. | Environment registration form and change logs. |
| Operations permissions. | Backend roles, ERP write scope, and fund permissions. | Separate price changes, refunds, withdrawals, and receiving changes from daily operations. | A single main account is shared by everyone, and anyone can make withdrawals. | Role list and offboarding recovery record |
These four layers are not four parallel techniques but a sequential chain: the legal entity determines how payment accounts can be set up, payment determines how funds are justified, the login environment determines whether operations can be traced, and permissions determine who to contact and what materials to obtain after an incident.
Payment accounts: Perform four consistency checks before considering multi-store expansion
- Entity consistency.The store registration entity, the payment account entity, and the invoice header on contracts must align. When using a third-party payment service provider, submit store authorization and entity proof as required. Do not borrow someone else's already-linked account as a temporary workaround.
- Explainable usage.Every incoming transaction in the account can be traced back to a specific order, logistics tracking number, and refund record. Large or high-frequency transfers that clearly do not match your store's product category make it difficult for risk control systems to determine the nature of these funds.
- Reconcile and archive statements on a monthly basis.Prepare a separate reconciliation statement for each store covering orders, incoming payments, and refunds. Retain these records for a period that covers both the platform's inquiry window and the tax requirements of your region; do not wait until you are asked for information before going back to reconstruct the records.
- Keep primary and backup channels separate.Do not funnel all of your stores' funds into a single receiving account. In addition to your primary channel, maintain at least one verified backup channel. The purpose of the backup channel is to ensure continuity of cash flow, not to open a large number of unassociated accounts.
The boundaries are clear: do not use personal accounts to receive payments for business stores, do not fabricate transaction backgrounds, and do not borrow or buy and sell other people's accounts. Once these lines are crossed, the subsequent comparison tables and reconciliation statements will be meaningless.
What to Do First and Second After Your Payment Account Is Frozen
People who search for “what to do if your cross-border e-commerce payment account is frozen” often make the first mistake: repeatedly submitting the same documents. A more effective first step is to clarify three things—whether the freeze originated from the platform side or the payment provider or bank side, whether it is a risk-control review or a judicial freeze, and what specific document list and submission channels the relevant party requires. These three factors determine the direction of all subsequent actions and indicate whom you should contact first.
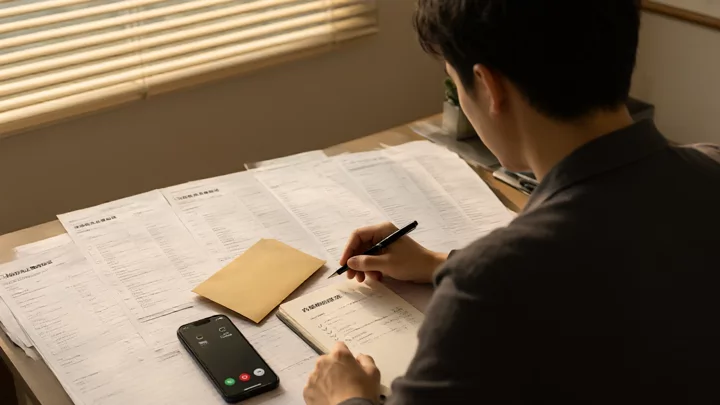
The four time segments shown in the figure are internal response targets, not guaranteed timelines from the platform or payment provider. A feasible sequence is: first, inventory in-transit orders, pending settlement amounts, and available cash flow to decide whether to pause ad spending or delay restocking; next, organize entity verification documents, store backend screenshots, recent order and logistics records, and refund/dispute records into a consistent set of materials; when submitting, provide only the specifically requested items, using a corresponding explanation for the platform, payment service provider, and bank respectively; after recovery, immediately verify whether account permissions and binding relationships have been altered.
If the freeze is accompanied by store account restrictions, the handling sequence and evidence organization can referencethe appeal and recovery process for cross-border e-commerce account suspensions, using the same set of materials for both, avoiding creating separate versions.
Login environment: the goal is auditability, not disguise
The goal of managing the login environment is not to make the platform “unable to tell it is the same person,” but to ensure every login is traceable to a specific person, device, and time. Each store should be assigned a fixed set of device, network, browser profile, and 2FA holder; register before switching computers, networks, or personnel. Emergency logins via public networks or backup phones are the most likely to create gaps in the audit trail.
When using a multi-account browser, treat it as a record-keeping tool: log the profile ID, corresponding store, responsible person, and last-used time. It records correspondences, not identity disguise; for specific capabilities, refer to each platform’s official seller help center regarding its multi-account policy. For troubleshooting wrong-store errors or incorrect price changes resulting from multi-platform batch operations, see the reference path below.Troubleshooting Guide for Multi-Platform Seller Account and Store Management Tools.
Write the correspondences into a table that can be consulted at any time
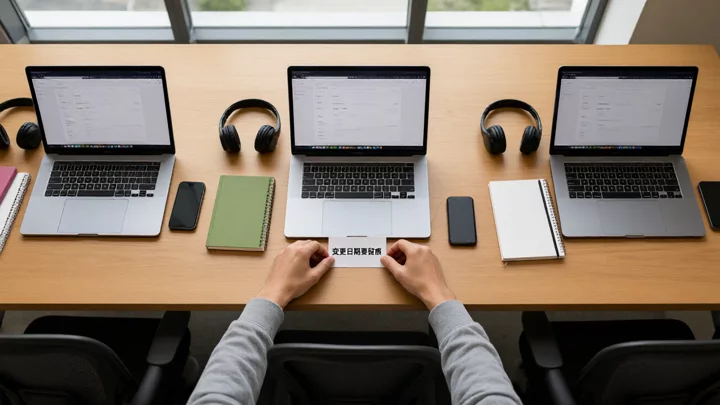
The most useful column in the table is the “Last Change Date.” When verification code anomalies, orders are recorded in the wrong store, or settlement delays occur, check this column first: if a store recently changed devices, changed the responsible person, or if 2FA was just transferred, the issue often lies there rather than in the tool itself.
Operational Division: Separate “money-changing” permissions from daily operations.
- Store Manager:Monitors platform performance, policy notifications, and account health status, serving as the primary point of contact for platform notifications.
- Operations:Responsible for listings, customer service, promotions, and ad placements, without holding permissions for withdrawal or payment account changes.
- Finance or Lead:Holds independent viewing and withdrawal access to the payment account and is responsible for monthly reconciliation. No matter how small the scale, this role should be held by someone who does not directly operate the store.
- Two-person confirmation:For price changes above the threshold, bulk refunds, withdrawals, and payment account modifications, two-person confirmation is required. Document the thresholds and approvers in the process.
- On the day of departure:Revoke backend roles, ERP accounts, browser profiles, and 2FA; update passwords and log the timestamp. Residual permissions are harder to detect than missing ones because they do not trigger errors.
Teams of two or three can also implement this division of roles, with one person holding multiple roles, but each role must be clearly defined and separated. For role allocation in small teams and store management basics, refer toPractical key points for TikTok Shop seller accounts and operational tools. For platform-level differences in multi-store structures, seeAlibaba, Shopee, Lazada, and Temu multi-account operations and store management tool audits.
FAQ
Can multiple stores share a single payment account?
Not recommended. Unless the platform and service provider explicitly allow it and the entity relationships can be clearly explained, sharing will make it impossible to match each fund transaction to a specific store. The minimum requirement is that each store has independent reconciliation statements, and backup channels are pre-approved.
When the platform requires video verification, what login environment records should be prepared?
Clearly explain who logged into the store, at what time, using which device, and over which network. Retrieve the environment log and 2FA holder records for cross-checking; do not temporarily change configurations to take screenshots just to meet verification requirements.
After a receiving account is frozen, should you contact the platform or the payment institution first?
Check who issued the freeze notification. If the notification comes from the payment institution or bank, follow its required documentation list; if it comes from the platform, first confirm in the seller dashboard whether it is an account restriction or a settlement delay. If both processes are running simultaneously, use only one consistent version of facts externally.
For a team of only two or three people, what is the minimum level of permission separation required?
Four items: separate viewing and withdrawal permissions for the receiving account from daily operations; do not bind 2FA to a single phone; require dual-person confirmation for withdrawals and changes to the receiving account; change passwords and record the time on the day of departure.

