

Logging in to multiple Shopify accounts at the same time does not in itself constitute a basis for a store being judged as associated. What the platform records are the environment and data signals collected at login—the same browser profile, the same egress IP, the same payout account, the same email. The more these overlapping items are, the higher the probability of being classified under the same operating entity. The login action is merely the point in time when collection occurs, not the reason for the determination.
So what really needs to be answered is not 'can they log in at the same time?' but 'at which layers do these stores share the same set of resources?' Below, we break it down by risk layer, then provide boundaries you can directly follow.
The 4 types of association triggers for multiple Shopify accounts
| Layer | Typical trigger point | Sensitivity | Troubleshooting order |
|---|---|---|---|
| Information and Payment | Same legal representative, business license, receiving account, return address, and customer service phone number | Highest | 1 |
| Network egress | Multiple stores share the same IP, or share neighboring IP ranges in the same data center | High | 2 |
| Browser environment | Same browser profile, shared Cookie and local storage, consistent Canvas/font/screen parameters | High | 3 |
| Operational behavior | Logging into multiple admin panels in batches from the same device at fixed times and copy-pasting identical product listings and copy | Medium | 4 |
These four layers are not parallel. Account details and payment belong to the entity layer and carry the highest weight; once they overlap, there is almost no room for explanation. Network egress and browser environment belong to the environment layer and are signals continuously collected by the platform during login and sessions. Operational behavior alone is not enough to classify the account, but it stacks with the first two layers and amplifies the overall risk score. How the platform ultimately handles the matter is subject to the notifications in the account and official policies; no single signal necessarily leads to a ban.
Operational boundaries: what can be shared and what must be isolated
Spelling out the boundaries is more useful than repeatedly stressing “be careful about security.” The following is listed by field, and there is only one criterion: whether this field would point two stores to the same entity or the same device.
- Store domain: Each is independent; this is a natural isolation item on the Shopify side and requires no additional handling.
- Registration email: Must be independent. Using the same email for registration or as a recovery email is the easiest link to make.
- Payment account: Multiple stores under the same entity can reasonably share one, but if you want to be treated as an independent entity, payment must be separate.
- Egress IP: Each store should have a fixed, independent egress IP, and avoid the same data center segment as much as possible. Logging into multiple stores over a shared home broadband is a common high-risk scenario.
- Browser environment: One profile per store; cookies, local storage, and cache must not overlap. Multiple windows or multi-user profiles in a regular browser do not satisfy this requirement.
- Staff permissions: The same team collaboration workflow can be shared, but each employee's account should only be granted the permission scope for that store. Specific permission items shall be subject to the Shopify Official Help Center instructions.
- Customer service phone number and return address: Can be shared within the same entity, but must be separated across entities.
Domains and email addresses are low-cost isolation items. Complete these two first before discussing fingerprints and proxies; reversing the order often means wasting money.
Real risk comparison of three common login methods
| Login method | Environment-level risk | Entity-level risk | Use cases |
|---|---|---|---|
| Switching accounts in the same browser | High: Cookies, local storage, and fingerprints are fully shared | Unchanged, depending on whether the email and payment collection are shared | Daily operations of employees within the same company checking their own stores |
| Different browsers + same IP | Medium: storage layers are separated, fingerprints are still highly similar, and egress is the same | Unchanged | Temporary emergency access, not suitable for long-term multi-store operations |
| Independent environment + independent IP | Low: independent profile and independent egress per store | Depends on whether email and payment collection are independent | Long-term operations with multiple entities and multiple stores |
Minimum isolation configuration: one environment per store
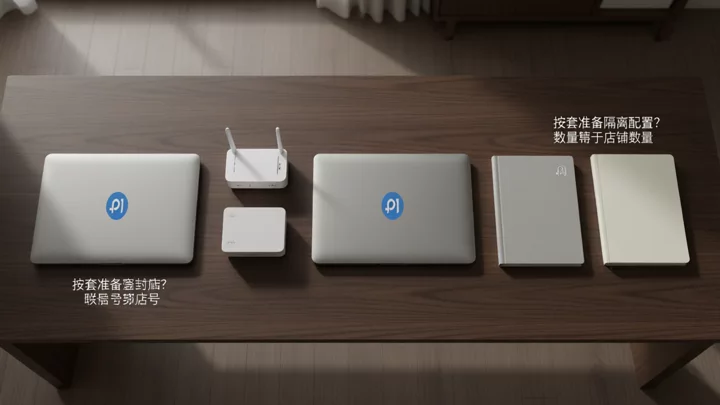
Implementation does not need to be complex. The minimum actionable configuration is: one independent browser profile per store, bound to one fixed proxy egress, corresponding to one independent email and one independent payment collection; five stores mean five sets, with no borrowing between them. For team collaboration, staff duties are divided by store, not cross-authorized by function.
If multiple stores frequently trigger CAPTCHA pop-ups or account abnormality warnings, first follow Browser isolation and network environment troubleshooting for multi-store logins that keep getting flagged by risk control and start from the network layer—this usually helps you pinpoint the problem faster than switching tools right away. For tool-level selection criteria and first-time configuration methods, see How to Choose and Use an Antidetect Browser.
If association warnings have already appeared, handle them in this order
- Immediately stop logging into the affected stores from the current environment, including using a mobile browser to check the backend temporarily.
- Check the original text of the notification in the account to confirm whether the reason given is an abnormal environment, overlapping information, or something else—do not judge based on guesswork.
- Review login records and permission lists to identify the fields still shared across multiple stores, and prioritize payment collection, email, and IP.
- Only resume operations after the shared items have been fully separated. In the early stage of resuming, limit the frequency of batch actions to avoid handling multiple stores in the same time window.
- When you need to file an appeal, submit materials through the official channels, explain the entity relationship and the isolation adjustments already completed, and keep a record of your communications.
If your store portfolio includes both Shopify and Amazon accounts, the risk priorities on the two sides are not the same; for role and permission plans you can refer to Comparison of Managing Multiple Shopify Stores and Multiple Amazon Accounts,avoiding mixing the two sets of logic into one.
Frequently Asked Questions
If I use the same computer but different browsers to log in to multiple Shopify accounts, will they be linked?
Different browsers keep cookies and local storage separate, but their fingerprint characteristics are highly similar, and the outbound IP is usually the same as well. This is safer than switching accounts within the same browser, but it does not equal isolation. Whether accounts are judged to be linked depends on the combination of signals the platform collects, and its notification is the final word.
Can multiple Shopify stores use the same payout account?
A payout account is an entity-level signal, and sharing one explicitly binds several stores to the same payout entity. If the stores already belong to the same company, sharing is reasonable; if you want each store to be operated as an independent entity, the payout accounts must be kept separate.
How risky is it to register multiple stores using the same person's identity information?
Multiple stores under the same legal representative or the same business license are naturally regarded as the same entity from the platform's perspective. Whether they are permitted depends on the platform's specific policy on multiple stores, and "registration successful" cannot be used as the basis for a safety judgment.
Can an antidetect browser 100% prevent Shopify multi-account linkage and store suspension?
No. It only handles the browser environment layer; proxies handle the network egress, while entity information, receiving accounts, and operational cadence are outside its capabilities. Tools that claim to provide complete anti-association protection can be ruled out immediately.
After a store is banned due to association, can the account funds still be withdrawn?
There is no universal answer; it depends on the platform's specific decision regarding the account and its current status. First check the notifications and official instructions in the account, then submit materials through official channels to appeal. Do not repeatedly register new stores to test.