


After switching stores in Seller Central, secondary verification pops up frequently, the ERP changed the price of Store A to Store B, and an employee who left two weeks ago can still use their old account to delist products—these phenomena are often dismissed as "insufficient tool features," but switching to a different software often does not resolve them. The real cause is usually that a fixed correspondence has not been established between the account entity, Seller Central roles, login environment, and the tool's write scope. The tool merely amplifies this misalignment into batch operations.
Therefore, the first step in selection is not to compare feature lists, but to first determine at which layer the problem lies, and then apply the same set of standards to verify browsers, ERPs, and multi-store management tools. Whether the write scope is controllable, auditable, and revocable is more worth verifying on the spot than the buzzword "anti-association."
First, make it clear: Is it a confusing account structure or poorly performing tools?
Before deciding to switch tools, first use three on-site signals for a preliminary judgment to save a lot of trial-and-error costs.
- Frequent secondary verifications:Using the same computer and the same employee, the verification frequency is significantly different when logging into different stores, which indicates that the login environment does not have a one-to-one correspondence with the stores, or that the login behavior appears anomalous to the platform.
- Same operation producing different results across stores:Even with the same bulk price update, some stores succeed while others throw errors or modify different fields, which usually means the tool's authorization scope covers multiple entities.
- Cannot find the logs after a bulk operation:If you cannot clearly identify who made the changes, what was changed, or how many SKUs were affected, it means the write process lacks preview and rollback mechanisms; tools like this pose the highest risk when expanding store operations.
If only one of the three signals appears, it is often a configuration issue that can be resolved by adjusting permissions and environment mappings; only when two or more signals appear simultaneously should you consider switching tools.
Amazon seller accounts, Seller Central, and multi-account boundaries
These three are often confused with one another, but they have different boundaries and correspond to different management actions.
- A seller account represents the business entity and regional account.Per Amazon's official seller announcements, typically one account is operated per regional marketplace, and multiple accounts may be held when legitimate business needs exist. Accounts should be maintained in good standing, as policy issues on one account may impact related accounts. Therefore, for multi-account management, the primary focus should be on entities, marketplaces, and performance—not just logins.
- Seller Central is the operational backend, not the account itself.Role permissions, notifications, performance metrics, and appeal materials all flow through this platform. When an employee departs, their user permissions must be revoked in Seller Central; merely changing the password is insufficient.
- Compliant multi-account management requires handling four key areas:Correspondence between entities and marketplaces, archiving of performance and appeal materials, clear separation of receiving and tax entities, and controlled tool write access. Addressing only the login environment does not resolve compliance issues.
For a complete breakdown of how account entities and backend roles are divided, seeAmazon Seller Account and Seller Central Usage Overview. For the official wording on multi-account and linkage impacts, refer tothe Multi-Seller Account Announcement on the Amazon Seller Forumto verify the original text.
Pre-screen shop management tools with five acceptance checks
The following five items can all be verified on the spot during the trial period, without relying on sales demonstrations.
- One-to-one mapping between account entities and shops:A single shop record in the tool must be tied to only one entity and one site; a scenario where "one authorization manages three shops" must not occur.
- Role-based permissions aligned with Seller Center roles:The data visible and actions executable for operations, customer service, and finance teams should differ, rather than granting admin privileges to everyone.
- Isolated and auditable login environments:You can trace exactly who logged into which store, when, and from what environment.
- Batch writes include preview, rollback, and logging:Before changing prices, syncing inventory, or delisting, you can see the impact scope; if errors occur, you can roll back by batch.
- The permission model is scalable when expanding to new platforms:Adding a new TikTok Shop or Shopify store does not require disrupting the existing role configuration.
These five items andCompliance and Data Management for Multi-Account Operations on AmazonThe approach is consistent: define the mappings first, then discuss automation.
Draw the Requirements as a Four-Layer Mapping Diagram
Before selection, first map your existing stores onto a single four-layer diagram. From top to bottom, the layers are the account entity, Seller Central roles, the login environment, and the tool write scope. Each layer only allows one-to-one or one-to-many mappings; cross-layer intersections are not permitted. Common misalignment points are concentrated in the following areas: multiple stores under the same entity sharing the same administrator account; an ERP API authorization scope that is larger than what operations actually require; a login environment not fixedly bound to the store, allowing anyone with the link to log in; and write permissions granted at the intern level.
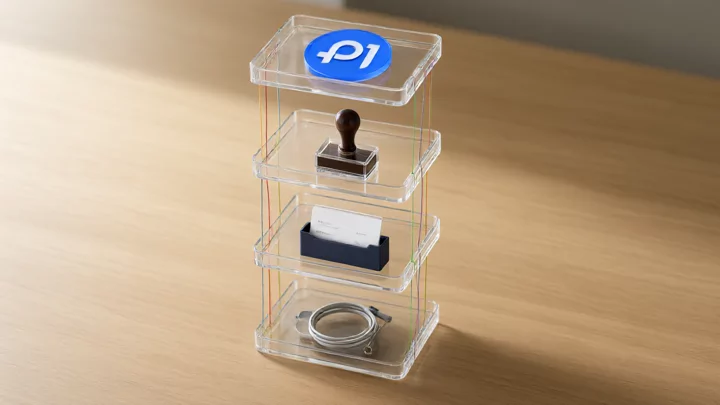
The value of this diagram lies in its ability to quickly pinpoint which layer is responsible when issues arise: frequent CAPTCHA challenges usually stem from the login environment layer, incorrect store targeting falls under the write scope layer, and incomplete permission revocation points to the role layer. Once you have identified the layer, you can determine whether the solution requires configuration adjustments or a tool change.
Select based on team stage: single store, few stores, multi-platform matrix
The minimal tool combinations differ significantly across stages, and introducing heavyweight systems too early only increases configuration overhead.
| Stage | Store Scale | Minimal Tool Combination | Priority Validation |
|---|---|---|---|
| Single Store Start | 1 store | Official backend + lightweight order/inventory tool | Whether write logs are complete and can be traced back by batch |
| Few Stores | 2 to 5 stores | Separated administration + environment isolation + unified account ledger | Whether the entity and stores have a one-to-one mapping, and if there is any residual access after permission revocation |
| Multi-platform matrix | More than 6, cross-platform | Unified ledger + role templates + write approvals | Whether cross-platform role reuse affects existing stores |
The 2 to 5 store range is the most prone to issues: the number of stores has already exceeded human memory capacity, but the team has not yet established processes. The focus at this stage is not the level of automation, but whether the three items of access control, auditing, and write scope can be implemented.
Conduct a controlled write test during the trial period
Do not test tools directly on live stores. Follow the four steps below; one round will generally help determine whether this tool is suitable for long-term use.
- Set up a test store or test SKU, using items that do not affect official listings as samples.
- Grant minimum permissions only: start with read-only access, then add write permissions item by item, such as price changes, inventory updates, and delisting, to avoid opening all permissions at once.
- Execute price changes, inventory synchronization, and delisting in sequence, verifying the preview results, execution logs, and rollback effectiveness at each step.
- Revoke authorization and log in with a different account to ensure no residual permissions or cached sessions remain before reconnecting the official store.
If you are already experiencing frequent verification or operational restrictions on your official store, first followtroubleshooting guidelines for restricted Amazon seller accountsto mitigate losses. Do not bulk update profiles or submit consecutive appeals during the restriction period, as this will further complicate the audit trail.
When expanding to platforms like TikTok Shop and Shopify, first separate platform store assets from standalone website assets.
Platform-based stores and independent sites operate on fundamentally different permission models; simply applying the same role templates is often the starting point for cross-store data leakage.
TikTok Shop, eBay, Walmart, Etsy, Temu, AliExpress, Shopee, Lazada, and Mercado Libre form a platform store matrix: opening a store is subject to recruitment and review constraints, operations are governed by seller center performance rules, and team collaboration requires permission division on the platform side. Taking TikTok as an example, the official recommendation is to use Business Center roles and permissions to assign members access to assets that align with their roles, rather than sharing login credentials.
Shopify, on the other hand, represents sellers' own independent site assets: multiple sites correspond to self-owned business units, and the management focus is on employee permissions and the scope of app authorization; refer to Shopify's Official Help Center.descriptions regarding store members and permissions on eBay. The entry points for eBay seller rules and store features are concentrated in the eBay Seller Center, which do not share the same permission logic as independent stores.
In terms of configuration, account ledgers should be split into at least two tables: one for platform stores (entity, site, audit status, performance) and one for own site assets (site, employees, app authorization). The differences between these two types can be compared using eBay, Walmart, Etsy multi-account tool comparison and TikTok Shop and Shopify multi-account collaboration. Do not force a single role template to apply to both.
FAQ
I only have two Amazon stores, do I need a dedicated multi-store management tool?
Check whether the three signals mentioned earlier appear. If operations are conducted by two or fewer people on a single site with no need for batch price updates, adding a lightweight order inventory tool to the official backend is sufficient, with emphasis on permission logs and store ledgers; consider an upgrade only when batch operations or multi-person collaboration begins.
How should anti-association browsers, ERPs, and store management tools be divided?
Browsers primarily address the login environment layer, ERPs handle the data and write layer, and store management tools cover the role and ledger layer. These three overlap in write scope, which is also where errors most commonly occur. It is recommended to select only one as the single source of truth for account ledgers, with other tools retrieving authorization from it.
Isolated environments are already in use, why does secondary verification still pop up?
Trigger factors are not limited to the environment; they may also relate to sudden changes in login time and location, device changes, or the account's own performance or review status. Platforms typically do not fully disclose reasons for enforcement actions externally, so account notifications and official policies should be the reference; stop batch operations first, then investigate.
Expanding to TikTok Shop or Shopify, which configurations need to be redone?
Role templates, store ledgers, and write approvals all need to be redone per platform. Platform stores focus on reviews and performance, while independent sites focus on employee and app authorization; the granularity of privilege separation differs between them. Processes can be reused, but the same role definitions cannot be reused.

