


Logging into Amazon seller accounts and TikTok Shop seller accounts separately works fine, but when teams collaborate on order processing, price changes, and customer service, frequent CAPTCHA pop-ups and ERP data being written to the wrong store become increasingly common. This is usually not caused by the number of stores, but by a lack of fixed correspondence among the four layers: account entity, seller central role, login environment, and tool writing. Establishing a clear mapping architecture is the foundation for resolving the chaos in multi-platform, multi-account operations.
This article will break down the permission architecture differences of mainstream platforms, provide isolation standards for fingerprint browser and proxy configuration, and offer a troubleshooting checklist for ERP tool selection.
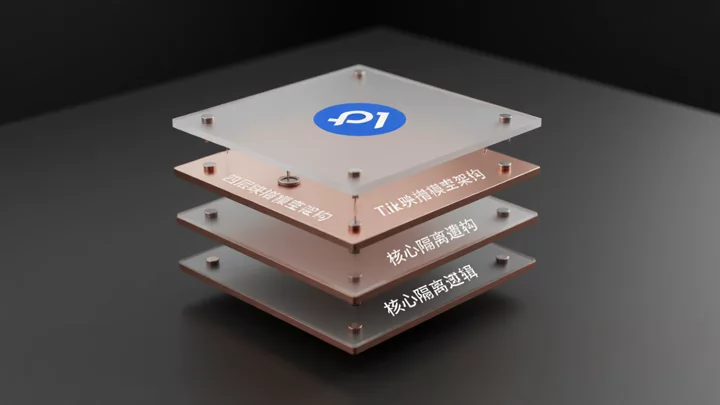
The Four-Layer Mapping Model: The Underlying Logic of Multi-Platform Account Isolation
To resolve the root cause of multi-account cross-contamination, it is necessary to build a mandatory "four-layer mapping" system. These four layers must correspond one-to-one; any misalignment in any layer will cause conflicts between operators, system data writing, and platform risk control signals.
- Account Entity: A clearly defined legal entity or individual industrial and commercial household, which determines your compliance boundaries and responsible entity on each platform.
- Backend Role:Specific permission levels assigned in the Amazon Seller Central, TikTok Shop Seller Center, or Shopify (e.g., admin, finance, customer service).
- Login environment:The isolated fingerprint environment, proxy exit, and operating system attributes for the specific account being operated.
- Tool write-through:The explicit account designated in the ERP or store management tool to receive orders, inventory, and price change instructions.
Comparison of permission architectures across major platform seller centers
The boundaries for back-office roles and multi-account management vary significantly across different platforms. TikTok Shop's permission management relies on the TikTok Business Center, emphasizing team asset isolation; Amazon enforces strict correlation reviews for the health of multiple selling accounts; and Shopify focuses on binding employee accounts with independent site asset management. When operating cross-platform, one must never simply apply a single permission model.
| Platform Type | Back-Office Roles and Permission Management Boundaries | Core Considerations for Multi-Account Isolation |
|---|---|---|
| TikTok Shop | Rely on the access scopes assigned by the Business Center that match specific roles, and never share login credentials. | Strict separation between advertising assets and store operational assets; the environments must remain isolated. |
| Amazon | Role permissions inside Seller Central, with attention required to the independent operational status of multiple accounts. | Prevent cross-account data leakage; the login environment must ensure fingerprint and IP isolation. |
| Shopify | Manage assets within the independent store based on the division of permissions between the store owner and employees. | Ensure that the write path for store management tools strictly corresponds with the store owner account. |
When configuring TikTok Shop, sellers should standardize team access by following the official [TikTok Roles and Permissions Guide](https://ads.tiktok.com/help/article/about-business-center-roles-and-permissions?lang=en "TikTok Roles and Permissions Guide").
Environmental isolation boundaries for fingerprint browser and proxy configurations
The login environment is the most easily overlooked layer in the four-layer mapping. A fingerprint browser is a core tool for resolving cross-platform account environment conflicts, but its role is solely to reduce the probability of session hijacking and fingerprint collisions; it must never be used as a 'get-out-of-jail-free card' to bypass platform risk controls.
When selecting a fingerprint browser and configuring proxies, clear isolation boundaries must be defined. Proxy exits should not only achieve one store, one IP, but also ensure that the IP location aligns with the actual operational logic of the account entity. For team environments, it is essential to ensure that the fingerprint environment has audit capabilities to reconstruct specific operations. For detailed breakdowns of security boundaries and compliance risks in multi-account environments, refer toMulti-Account Operations with Fingerprint Browser: Securitydetailed assessment.
Selection and Verification Criteria for Store Management Tools and ERP
The core of selecting an ERP or store management tool lies in the accurate implementation of the "tool writing" layer. Many sellers experience issues during data import because of missing underlying mapping tables, which can result in Amazon seller account orders being incorrectly written to TikTok Shop or triggering cross-store permission conflicts.
- Establish Mapping Tables: Manually establish fixed correspondences between account entities, platform stores, and operator IDs within the tool.
- Interface write verification: For each SKU or small-batch test order, verify that the store code written back by the ERP matches the preset exactly.
- Anomaly troubleshooting path: When frequent CAPTCHA prompts occur, immediately check for proxy session collisions, fingerprint tampering, or unauthorized operations by employees.
If you encounter data crossover issues when configuring cross-platform multi-account management tools such as Amazon, TikTok Shop, or AliExpress, you can combineMulti-platform, multi-account operations seller tools troubleshootingGuide to make repairs.
Warnings on multi-account association risks and compliance boundaries
Platform policies explicitly state that typically, one account should be operated per region; multiple accounts are permitted only when there is a legitimate business need. Accounts should be maintained in good standing, and policy violations on one account (such as fake orders or non-compliant shipping) may trigger consequential actions against associated accounts. Before designing a multi-account architecture, be sure to refer to the2024 Cross-Border E-Commerce Compliance Policy Checklistto verify reporting, tax, and account environment requirements for each platform.
Frequently Asked Questions
Common Questions
Can a fingerprint browser 100% prevent platform association and account bans for multiple accounts?
No. A fingerprint browser only isolates device characteristics at the network level and cannot change fund flows, IP attribution, or compliance entity logic. Multi-account compliance must strictly follow the official rules of each platform and business rationality.
Do teams handling both Amazon and TikTok Shop need to set up two separate permission systems?
Yes. The account structures of the two platforms are not interchangeable. TikTok Shop manages digital assets and ad allocations through the TikTok Business Center, whereas Amazon relies on its internal seller center account structure. The two systems must be configured independently.
Why do ERP tools consistently throw errors or produce disorganized data when syncing multiple stores?
This is usually caused by the lack of a fixed mapping between the “account entity” and “tool write operations.” When the tool retrieves API tokens from various platforms, it fails to identify specific store IDs and their corresponding entities, resulting in data being written to the wrong stores. The underlying mapping table must be cleaned up first.
How does switching a reseller's IP affect multi-account operations?
Switching resellers may cause the IP's geographic origin to mismatch with the account entity's location, potentially triggering the platform's risk control system to intervene in “abnormal logins.” It is essential to ensure that the proxy IP remains stable and consistent with the long-term operational geographic profile of the account.

