


What is truly difficult in managing Amazon multi-account operations is not tool functionality, but whether four things are fixed and correspond correctly: who owns the store, who has what permissions in Amazon Seller Central, from which login environment they access it, and which stores and fields the ERP can modify.
When these four layers are misaligned, individual store logins may function normally, but once the same team centrally handles orders, price adjustments, and customer service, frequent verification prompts, inventory updates written to the wrong stores, and lingering permissions of departed employees will surface together. The following expands on these four layers, first defining compliance boundaries and permission responsibilities, then explaining how to integrate Amazon store management tools, and finally providing a checkable list of related risks.
First, identify the issue: Why does chaos begin after centralized management despite single-store normalcy
Look at three symptoms: The same account logs in stably on a fixed computer, but frequent verification is triggered upon changing users or networks; batch price and inventory updates target the wrong store; after an employee leaves, sub-accounts, ERP accounts, or two-factor authentication remain active. These issues fall into the login environment, tool write, and permission revocation layers respectively. They are not the same type of failure, and switching tools usually does not resolve them.
Four-Layer Mapping: Account Entity, Seller Central Roles, Login Environment, and Tool Write
- Account EntityDetermines store ownership, qualifications, and compliance responsibilities; it is the root of whether multi-account operations can be established. A common misalignment is registering stores in different regions using the same set of information without registering their respective qualifications, payment, and responsible parties.
- Seller Central Role: Determines what a user can see and modify after logging in. A common misconfiguration is all operations staff sharing the store owner's account, or granting permissions for ads, refunds, and inventory all at once.
- Login Environment: Determines which device, network, and browser configuration are used to access the account. A common misconfiguration is multiple people taking turns logging into multiple shops on a single computer, or mixing local and remote desktop usage.
- Tool Write Access: Determines which stores and fields a store management tool can modify. A common misconfiguration is checking all stores and all fields during authorization, enabling write access directly during the trial phase.
The judgment standard is simple: one layer solves one type of problem. Do not solve permission misconfigurations by changing the network, and do not solve login verification issues by changing roles.
Compliance Boundaries for Amazon Multi-Accounts: Legitimate Business Needs and Related Impacts
According to Amazon's official seller announcements, typically one account is operated per region; multiple accounts can be held if there are legitimate business needs; accounts should maintain good standing, and policy issues with one account may affect related accounts. In other words, having multiple accounts is not the problem itself; the problem lies in whether the entity is real, whether the business needs are clearly explained, and whether account health is maintained synchronously. No tool can replace this step, nor should you expect to bypass platform reviews using tools. Rules will change, so refer to the latest policies in Seller Central and account notifications.
The basis for verification can be seen at Amazon's official guidelines on multiple selling accounts and account health.
How to switch Seller Center permissions and integrate store management tools
- Create roles by position: Build a set for each function—operations, customer support, finance, and logistics. Do not create roles by name; document roles and responsibilities in the permissions matrix.
- Start with least privilege: Grant customer support access to orders and messages only, finance access to settlements and reports only, and allocate operations access by marketplace. Issue advertising permissions separately.
- Secondary confirmation for sensitive operations: Require a second person to review or conduct post-event spot checks for any of the following: price changes, inventory updates, refunds, delisting, or changes to payment details.
- Integrate only necessary stores and fields: Start with one store using read-only order synchronization. Verify that store names and marketplaces correspond correctly before adding stores incrementally.
- Run read-only first, then enable write accessObserve the sync results for a few days, verify that the backend and tool data are consistent, then enable price and inventory updates.
- Keep logs and set up revocation pathwaysMake it possible to audit who changed which fields in which store and when; ensure offboarding procedures cover seller center roles, ERP sub-accounts, and two-factor authentication devices.
Select Amazon seller tools based on four criteria rather than counting feature lists: whether write access is limited to specific stores and fields, whether operation logs and approvals exist, whether long-term logins frequently trigger verification, and whether permissions can be revoked in one step when roles change or staff leave. For selection details, refer toAmazon Seller Center and Multi-Account Operations: How to Choose Store Management Tools; if you are still comparing ERPs,Choosing Between DianXiaoMi and Mango Store Manageroutlines the decision order based on platform focus and team size.
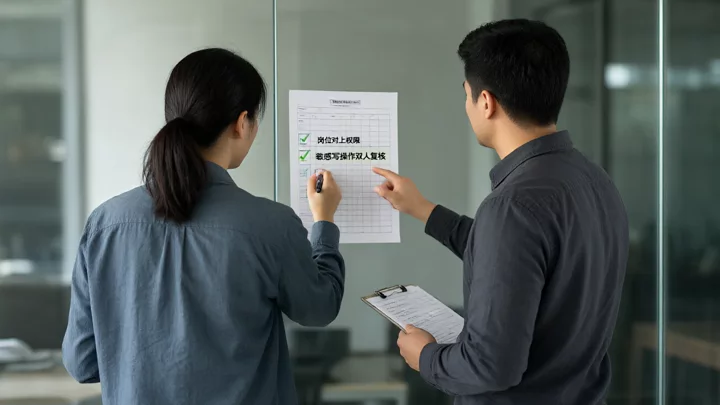
Related risk checklist: Before tool deployment, Daily, Personnel Changes
Before tool deployment
- Each store's registration entity, site, payment method, and responsible person are documented; the passing evidence is that the ledger matches the account information in the Seller Center.
- Specify which device, which network, and who is authorized; new device access requires an application; the passing evidence is the device and network usage records.
- Set Seller Center roles by job function and enable two-factor authentication; the passing evidence is that the role list and personnel roster correspond one-to-one, with no shared store owner accounts.
- Tool authorization specifies the store and fields, with write access disabled by default; the passing evidence is that configuration records identify which fields are not opened.
Daily
- CAPTCHAs and login anomalies are archived by person, store, and time; when they appear in clusters, suspend bulk operations first.
- Price changes, inventory changes, and refunds—the three types of write operations—are spot-checked daily to verify the target store is correct.
- Price and inventory changes are traceable to the operator and specific task number, allowing rollback when anomalies occur.
Personnel changes
- Revoke Seller Center roles, ERP sub-accounts, corporate email, and two-factor authentication devices on the day of departure.
- Reset shared passwords and confirm no roles have been transferred to others.
- Recheck login logs one week later to confirm there are no residual sessions or abnormal logins.
Frequently Asked Questions
How should I assess the risk of account association when using the same set of documents for multiple Amazon marketplace stores?
The key is not the number of stores, but whether you can clearly explain the entity and business needs, and whether account health is maintained in sync. Accounts under the same entity may have policy issues that affect each other. First, manage store ledgers, login environments, and permissions separately, then assess the risks.
ERP allows bulk price changes. How can I prevent writing to the wrong store?
Limit write permissions to specific stores and fields. Before executing a bulk task, verify the correct store using one test SKU. Require a second person to review price-change operations and retain task numbers in the logs to facilitate rollbacks.
Is it enough to just change the password when an employee leaves?
No. The password is only one entry point. You must revoke access to Seller Central roles, ERP sub-accounts, two-factor authentication devices, and corporate email sessions, then review login logs one week later.
If I am already undergoing an association audit, should I appeal first or organize permissions first?
First, stop the loss: pause bulk write operations and new logins. Organize entity documentation, store ownership, and operation records, then submit according to the account notification requirements. See the investigation order inComplete handling approach for restricted Amazon seller accounts.

