

Starting on the third day, CAPTCHAs for backend login became more frequent than usual; on the seventh day, an employee said they saw an abnormal login alert; later, a linkage risk notification landed on one of the stores. This sequence is not a coincidence: platforms rarely determine linkage based on a single action; instead, over several days they stack multiple layers of signals until their overlap exceeds what the platform is willing to tolerate.
So the focus of troubleshooting is not "Is my IP clean?" but "among the four signal layers, how many simultaneously point to the same identifiable entity?" Below, we first break these four layers apart, then provide a 30-minute self-check process you can complete and red lines for asset sharing. If your past experience was managing three stores from the same computer, you can first compare it with a small team of two or three people.From Chaotic Logins to Stable Operations: A Multi-Store Practical Recap, to see at which step you are stuck.
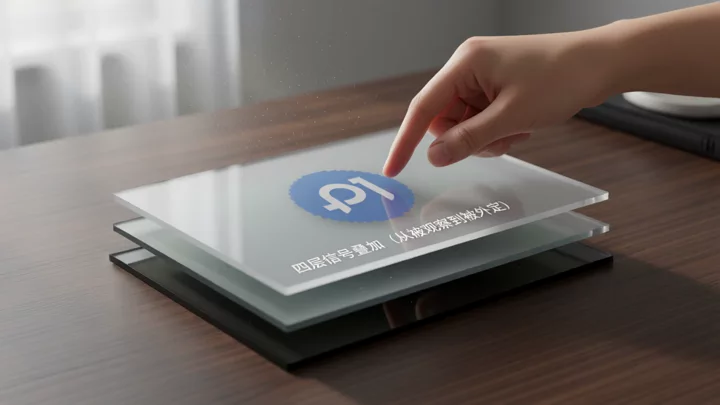
The four layers of signals platforms use to determine linkage, examined layer by layer.
Any single layer overlapping on its own usually only puts the account into an observation state, such as more CAPTCHAs or frequent requests for secondary verification. Actual determination usually occurs when two to three layers overlap at the same time within the same period.
- Login credential layer.Account passwords, two-factor authentication methods, recovery email addresses, and phone numbers. Two stores sharing the same recovery email address, or both being linked to the same group of employees' phone numbers, is the most easily overlooked overlap.
- Network egress layer.The type and ownership of the IP, and how many stores are logging in through this egress at the same time. Residential IPs and data center IPs have different observation weights, but sharing is more critical—when multiple stores log in through the same egress on the same day, the signal is significantly strengthened.
- Browser and device environment layer.Cookies, time zone, language, fonts, screen, and hardware parameters. Once an environment has been copied, both environments will go live with the same underlying parameters, and no matter how many times you change the password afterward, it cannot be cleared.
- Profile and behavior layer.Entity information, receiving accounts, return addresses, customer service email addresses, as well as customer service scripts and new product launch cadence. This layer can be cross-compared without any technical means.
Broadening the scope makes it clearer: risk control monitoring is never about the number of stores itself, but about the degree of overlap in login environments, network egress, and profile data. This point appears inPlatform Risk Control Rules and Compliance Essentials for Cross-Border E-Commerce Multi-Store Operationswhich contains a more detailed breakdown.
30-minute environment self-check: complete these four steps in order
- First, check the network exit.List the exit currently used by each store, note its location and type, and then count "how many stores have logged in under the same exit in the last 7 days." One store per exit is acceptable; two stores occasionally sharing one is suspicious; three or more stores regularly sharing one on the same day must be changed immediately.
- Next, check the browser environment.Confirm one environment per store, and that the environment was not copied from another store. How to check: after creating a new environment, compare its time zone, language, and font list item by item with existing environments; an exact match usually means it was copied.
- Next, check login credentials and the recovery chain.Check the bound email, phone number, and two-factor authentication device for each store one by one. If "two stores are bound to the same email" or "the recovery phone number is still held by a departed employee" appears, classify it as requiring immediate change.
- Finally, check the information layer.List the payment accounts, return addresses, customer service emails, and entity information in a table for side-by-side comparison. Reusing payment accounts across stores is the strongest overlap signal and takes priority over the other three items.
The goal of the self-check is not to fix everything the same day, but to first know which layer is blank. If you need to build a complete isolation structure from scratch, you can continue readingHow to Build an Account Isolation Solution for Cross-Border E-Commerce Stores.
Which assets must be one set per store, and which can be shared
There is only one criterion: whether this asset can enable the platform to link two stores to the same identifiable entity. If it can, it must be isolated; if it cannot, and it only circulates internally, it can be shared.
- Must be one set per store:Payment receiving accounts, return addresses, external customer service email addresses, store-bound mobile phone numbers and recovery email addresses, login environments, and network egress.
- Conditionally shareable:Employee personal accounts, asset libraries, and ERP backends. The condition is that sharing occurs only at the internal collaboration layer, and employee personal accounts gain access through the platform's official role and asset permission system, rather than sharing the same set of login credentials.
- Freely shareable:Internal documents, supplier contacts, and office equipment—as long as they do not enter the platform's view.
If you can no longer tell whether you are stuck at the credential layer, login environment layer, or collaboration permission layer, you can useMulti-store management tool selection comparisongo through the four tiers of capability boundaries in it, so you don't pay more yet still fail to solve that layer.
How do TikTok Shop, Amazon, and Shopify differ in their isolation criteria?
The most common mistake is to directly apply Amazon experience to TikTok Shop. The three platforms watch different layers, so the degree of isolation should naturally differ as well.
| Platform | Which layer risk control mainly focuses on | Can be shared | Must be one set per store |
|---|---|---|---|
| Amazon | Entity qualifications and account policy status | Login devices (within compliance scope) | Registered entity, payment collection, tax, and brand authorization |
| Shopify | Store members and permissions | Network environment | Employee accounts and permission scope |
| TikTok Shop | Shop backend + ad accounts + Business Center assets | Internal materials and documents | Login environment, network egress, Business Center roles and asset ownership |
Amazon's official position is that you typically operate one account per region, and may hold multiple accounts when there is a legitimate business need, but a policy issue with one account may affect related accounts, so its associated risk comes from the entity and policy status, not the login environment, see Amazon's official seller forum explanation on multiple selling accounts. Shopify's isolation focus, on the other hand, is on store members and permissions, and all feature entry points can be found at Shopify official Help Centerfor verification.
What really needs to be stepped up is TikTok: it officially requires assigning members access scopes that match their positions through roles and asset permissions, and avoiding shared login credentials, see Business Center roles and permissions guide. This means that store backends, ad accounts, and Business Center assets all come into view together. Isolating only store backend logins while letting three stores share one set of ad account permissions is one layer short. Ad delivery activities themselves are also required to comply with platform processes and local laws and must not interfere with reviews; this also applies to the delivery cadence of multi-store operations.
New store launches and personnel handovers are the two moments when overlapping traces are most likely to be left: a newcomer taking over an old environment, an old store's recovery phone number not being reclaimed, and Business Center members not being removed in sync will all come back days later in the form of login anomalies. The permission granularity and environment handover capabilities that should be confirmed at the selection stage are inthe collaboration dimension most easily overlooked when a team chooses a fingerprint browserthere is an item-by-item checklist.
Already received an association warning—what to do in the first 72 hours
Freeze first, then preserve, and only explain last.
- Freeze suspicious overlaps:Immediately stop switching the same exit or the same browser environment among multiple stores, and pin each store still sharing an exit to an independent environment one by one.
- Preserve evidence:Take screenshots of each store's current environment information, recent login records, and asset ownership, including Business Center members and asset lists, and ad account ownership.
- Resubmission notes:Reply through the channel specified in the platform notice, and clearly state the entity information, asset ownership, and isolation actions already completed; do not simply write "I did not violate any rules."
Do not bulk-edit information or bulk-file appeals before the investigation is complete—the changes themselves generate new signals and muddle records that could otherwise be clearly explained. If what you have received is already a termination rather than a restriction, the handling path is completely different; you can refer toGuide to Appealing and Recovering a Suspended Cross-Border E-Commerce AccountCross-Border E-Commerce Account Suspension Appeal and Recovery Guide
Frequently Asked Questions
If there are only two stores, will they still be deemed linked?
The number of stores itself is not the basis for the determination. If two stores share a payment collection account, a recovery email, and the same network egress, the number of overlapping layers is no different from that of five stores. First look at how many layers overlap, then look at the number of stores.
Is using a fingerprint browser foolproof?
No. A fingerprint browser only addresses the browser and device environment layer. If the network egress is still shared, recovery emails still overlap, and collection accounts are still reused, the remaining three layers will still stack up. It is a necessary layer, but not everything.
If the same customer service email is used, can the platform find out?
The customer service email used externally will appear in store profiles, email headers when replying to buyers, and after-sales records, making it a publicly visible association clue. We recommend one email per store; only email accounts used for internal routing can be shared.
After an employee leaves, can their environment and account be directly used by a new hire?
Not recommended. The old environment may already be bound to old two-factor authentication devices and login habits, and a direct handover is equivalent to bringing historical signals into the new hire's operations. The correct order is to first remove the former member's permissions and asset access, then have the new hire access the same environment using new credentials, rather than taking over the former member's account.
If a self-check reveals three layers of overlap, which layer should be changed first?
Prioritize by cascading loss: first cut off the shared network egress, then handle the payment receiving account and recovery email, and finally adjust the browser environment. The first two can be changed within a few hours; environment migration takes the longest but can be prepared in parallel.