

Store A's payout account was just flagged by the platform for 'abnormal association' and frozen. You're scrolling through your phone looking for the appeal portal while Store B's orders are still coming in and shipments are still going out. In those ten minutes, what actually broke wasn't the appeal process—it was that the isolation layer was never built correctly from the start. The exit IP and browser fingerprint are still shared, and the overlap across all four signal layers has long since crossed the threshold.
In Those Ten Frozen Minutes, Which Step of Your SOP Broke
Platform risk-control isn't a random 'false positive.' It monitors the overlap degree across four signal layers: login credentials, network exit, browser environment, and data behavior. When two or more layers stack up under the same exit IP or the same device fingerprint, the trigger leads directly to freezing the payout channel rather than sending a prior warning. For a 2–5-person team, the problem is usually not that there are too many stores to manage but that at the start you only isolated the account email addresses—exit and fingerprint were left untouched. First, cross-reference Multi-Store Account Isolation and Network Environment Self-Check Checklist to identify which layer has the gap, then decide whether to patch the isolation or go straight into the emergency process.
Isolation Isn't Just Changing Your Email: The Four Signal Layers Risk-Control Actually Monitors
- Credential Layer:Independent phone numbers, email addresses, and credit card BINs for each store. Criterion: no two stores share a common login phone number or the same card number.
- Network exit layer:Logins and daily operations for each store belong to different network segments or different ISPs. Criterion: a single Class C IP range shall not host daily operations for two or more stores.
- Browser environment layer:Independent browser profiles; Cookies, cache, and Canvas fingerprints do not cross between stores. Criterion: fingerprint detection tools confirm that no store's session carries another store's Cookies.
- Data behavior layer:Do not batch-export reports for multiple stores during the same time window, and do not store operating data for multiple stores under the same file path. Criterion: data belonging to a single store does not appear in another store's session records within the operation logs.
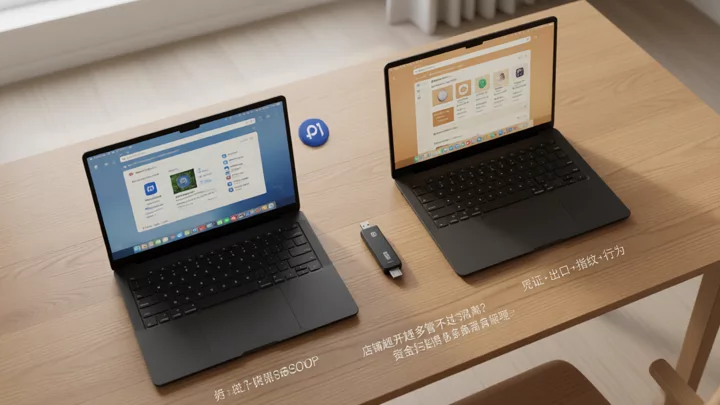
If any of the four layers is only "half-isolated"—for example, the exit IP is separated but the browser is not—overlap will still accumulate. Platform risk-control rules are updated quarterly, and existing solutions will not automatically remain effective. We recommend printing the Platform Risk-Control Rules and Compliance Key Points trigger-signal cross-reference table and posting it at your workstation; re-run the self-check after each announcement update.
Fund Consolidation: First, Figure Out Which Layer Your Cash Is Stuck In
The biggest hidden cost of running multiple stores isn't the extra deposits you pay—it's the same sales revenue being scattered and locked across three different entities. Consolidation starts with knowing where your money is stuck, for how long, and whether it should be moved.
| Fund Layer | Typical Hold | Consolidation Trigger |
|---|---|---|
| Platform Settlement Retention (Amazon 14 days / TikTok Shop 7 days / Shopify custom) | 3–14 days | Exceeds the platform's published cycle without reaching the in-transit account |
| Payment Processor in Transit (Payoneer / LianLian / WorldFirst) | 1–5 business days | In transit for over 7 days without crediting |
| Corporate bank account | Immediate | A single account balance falls below the next logistics payment requirement |
Consolidation does not mean "sweeping all funds into one account weekly." If in-transit funds exceed 7 days without settling, trigger an alert first and investigate the payment processor's status; only proceed with consolidation after confirming no technical failures. Payout cycles vary significantly across platforms—do not apply a single cadence to all. Specifically, refer to Multi-Shop Management Tool Selection Comparison to compare the fund-dashboard capabilities of each tool tier before deciding on upgrade milestones.
Three-Tier Inspection Cadence: Daily, Weekly, and Monthly
- Daily tier (30 minutes):Check each shop to confirm whether login sessions are active, and whether there is an abnormal surge in CAPTCHA requests or any risk-control pop-ups. Completion criteria: all shop back offices are accessible normally, with no unread risk-control notifications.
- Weekly tier (90 minutes):Export and cross-audit the outbound IP addresses and browser-fingerprint snapshots for each shop; complete fund reconciliation, flag in-transit items exceeding 7 days, and create tickets. Completion criteria: no new overlaps in the IP comparison table, and all in-transit anomalies have follow-up records.
- Monthly tier (half day):Review this month's risk-control trigger logs and update the isolation plan; verify tool permissions and collaboration handover status. Completion criteria: no over-permission items in the permission matrix, and all handover status fields are fully closed.
A three-person team can assign the daily tier to one person, the weekly tier to another, and run the monthly tier collectively. The key is to put 'who does what at which point in time' into the sheet rather than relying on verbal agreements. IP snapshots, reconciliation records, and permission-change logs left by routine inspections are the fastest appeal materials when a freeze occurs—refer to the handling path in Cross-Border E-Commerce Account Appeal and Recovery Guide's four-item checklist. If the team is still managing credentials and fund status with manual Excel spreadsheets, the upgrade decision can be informed by the Multi-Account Management module's capability boundaries for selection.
Frequently Asked Questions on Multi-Store Management
Does running three stores under the same legal entity amount to operating with 'zero isolation'?
No. The unit of assessment for platform risk control is the login environment and network egress point, not the registered business entity. As long as the four layers—credentials, IP, browser, and data behavior—remain independent across the three stores under the same legal entity, the overlap score will not automatically rise simply because the legal entity is the same. What is truly dangerous is the combination of 'same legal entity + same computer + same egress IP.'
How are in-transit orders and shipments for other stores handled during a freeze?
The frozen store stops placing new orders, but in-transit shipments continue to move. First, confirm whether the freeze affects the payment-collection channel or the order-placement permission: when only payment collection is frozen, shipments can still be dispatched normally; when only order placement is frozen, existing shipments are unaffected. Refer to the handling path in Account Freeze Appeal and Recovery the 72-hour action checklist.
Can a two-person team eliminate the monthly inspection?
Not recommended. The weekly cycle already covers IP and funds reconciliation; the core value of the monthly cycle is the “closed loop of the permission matrix and handover status”—when the team is small, these two items are the most likely to be skipped and the most likely to leave a gap during personnel changes. Keep the monthly cycle but compress it to 2 hours to cover the core items.
After a platform risk-control rule upgrade, do existing isolation schemes automatically become void?
They will not automatically become void, but the criteria will change. Platforms typically add new monitoring dimensions (e.g., expanding from IP to device fingerprint plus behavioral sequence). If your existing isolation only operates at the IP layer, overlap will re-accumulate under the new dimensions. Each time the platform publishes a risk-control update notice, rerunning the weekly fingerprint audit is the lowest-cost alignment step.