

When you reach the third store, you can still get by on memory; by the sixth, that no longer works. The problem is no longer "busy" but "wrong"—switching back and forth between backends, customer service sharing one set of login credentials, product copy reused across the entire store, until you receive a linked-risk warning and can no longer tell which layer of overlap caused it.
Multi-store management is mistakenly treated as a problem that requires more people and more tools. What truly needs to be done first is to separate three things: login environment, role permissions, and data definitions. If these three layers are not separated, the more people you have and the more expensive the tools, the more chaos will be amplified.
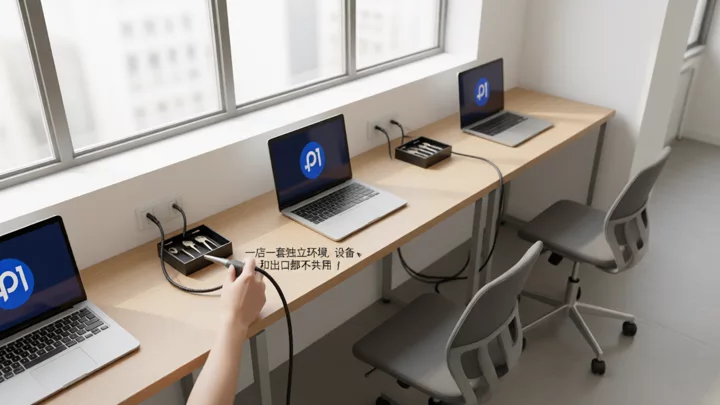
Account Isolation: Only When Four Layers of Signals Do Not Overlap Are Accounts Truly Separated
When a platform judges whether two stores are operated by the same party, it usually does not look at a single signal, but rather at the degree of overlap among multiple layers of signals. Self-checks should also follow these four layers.
- Credential Layer—Registration entity, legal representative information, payment collection account, bound phone and email. The easiest thing to miss is payment collection: two stores sharing one payment collection account is equivalent to tying the two lines together at the very first step.
- Network Egress Layer——Login IP and proxy nodes. Multiple store backends logging in from the same exit within a short time window is the most common source of overlap. A single overlap does not necessarily mean they will be judged as associated, but the platform records it; when combined with other signals, the risk rises.
- Browser environment layer——Cookie, local storage, User-Agent, time zone, and language. When the same computer uses the same browser to log in to accounts in turn, these parameters are naturally identical; logging in with a different account cannot separate them.
- Data behavior layer——Reuse of product images and copy, identical shipping and return addresses, consistent customer service script templates, and highly synchronized login times across multiple stores.
The detailed criteria for the four layers of signals and the trigger conditions for funds aggregation are inMulti-Store Management SOP from Account Isolation to Funds Aggregationfor a more complete breakdown; if your main focus is TikTok Shop, you can refer to TikTok Shop Multi-Store Environment Troubleshooting and Risk Self-CheckCheck item by item.
Permission division: split permissions by role, not accounts by store.
Small teams often go to two extremes: giving each person a store account, or using one account for all stores. With the former, no one takes over when someone leaves; with the latter, all stores' fuses are bundled into one. The right split is to grant permissions by role and assign data by store.
| Role | Can operate | Not available | Handover must be clearly documented |
|---|---|---|---|
| Operations | Product information, pricing, ad campaigns | Payment accounts, financial reconciliation | When changing product IDs or price-change effective times |
| Customer service | Orders, after-sales, on-site messages | Inventory and price changes | Open ticket IDs, committed response times |
| Content | Asset library, detail page drafts | Published prices and inventory | Asset version numbers, applicable stores |
| Logistics | Shipping system, tracking numbers | Pricing and advertising budgets | Exception order IDs, carrier channels |
| Finance | Collections, reconciliation, and reports | Product editing and advertising operations | Reconciliation cycle, discrepancy amount pending verification |
Login credentials for each store are issued only to the corresponding role, not as a "universal account for the entire store." Handovers do not rely on verbal communication; they rely on three fields: what is being changed, how far the change has progressed, and what time has been promised to the other party. For employee permission hierarchy and handover status field settings in the Shopify admin, refer to Shopify store management collaboration processes and permission settings.
Data review: daily anomaly checks, weekly structure checks, monthly profit checks
The most common mistake in multi-store reviews is looking at the GMV of all stores in aggregate. Once aggregated, an order surge at one store can mask two consecutive weeks of decline at another store.
- Daily: Focus only on anomalies, not totals. Refund rate, order cancellations, sudden spikes in ad spend, inventory alerts, out-of-stock SKUs. The question to answer is "which metric at which store deviated from its normal range today."
- Weekly: Look at structural changes. Traffic source share by store, conversion rate for key promoted SKUs, ad spend-to-output ratio, and fulfillment timeliness. Need to answer "which store's structure is changing, and whether it's changing for the better or worse".
- Monthly: Look at per-store profit. Gross margin, logistics costs, platform commissions, refund losses. Need to answer "which stores are making money and which stores are draining resources".
The premise is consistent definitions: same time range, same currency, same cost definition. For cross-platform stores, if even the settlement cycle and currency are not aligned, the period-over-period figures themselves are meaningless.
Tools and implementation: fix the weakest link first, then implement a system
Tools are not the starting point. First determine which layer is currently the first to fail, then decide what to buy; if you reverse the order, you are paying for a problem that has already been solved.
- The environment layer fails first(More CAPTCHAs, receiving association alerts): first fix the login environment, with dedicated egress plus one configuration per store; this is the prerequisite for all subsequent actions.
- The permissions layer fails first(Handovers rely on group chats, permissions rely on word of mouth): first use a shared spreadsheet to define role permissions and handover fields, then discuss buying a system.
- The data layer fails first(manually consolidating multiple back ends every day): then move on to an ERP or data dashboard to bring orders, inventory, and ads into the same framework.
- at 5 to 8 people and more than 8 stores: only then consider a combined solution of isolated environments, permission modules, and ERP, rather than buying a full suite of tools first and looking for use cases afterward.
what really needs to be compared during the selection stage is not the number of features, but the ad attribution methodology, whether inventory alerts can translate into replenishment actions, and whether data permissions are tiered; for reference, seeMulti-store management: from manual spreadsheets to a systematized tool selection comparison.
Frequently asked questions
Can multiple stores use the same payment collection account?
Not recommended. Payment collection accounts are an entity-level signal, and sharing them will significantly increase overlap. If conditions allow, bind them separately by store or by entity, and keep the withdrawal path clear and traceable.
Does a small team of two or three people also need to divide permissions?
Yes, but it can be simplified into two lines: who has the right to change prices and inventory, and who has the right to view payments and reconciliation. If these two are not separated, when problems arise you will not even be able to trace the operation records back to a person.
Is it okay to log in to multiple stores using different browser tabs on the same computer?
No. Tabs within the same browser share cookies and local storage, so at the browser environment level there is effectively no isolation. At minimum, make sure different stores use browser environments that are independent of one another.
Do you have to use a BI tool for data reviews?
Not necessarily. With three stores or fewer, a shared spreadsheet with a fixed structure is enough; the key is to define your metric definitions in advance. The motivation to upgrade your tools should come from the time cost of manual aggregation, not from a feature list.
Is it risky for beginners to open multiple stores right from the start?
The risk is on the high side, because neither the environment nor the process has been proven yet, and once you are judged to be associated, it may also affect the stores that are already live. It is advisable to first get the complete path for a single store running smoothly, from registration to first order, and then replicate it for the second store. You can refer toThe Complete Path and Common Pitfalls of a Cross-Border E-Commerce Getting-Started Tutorial for Beginners.