

On the seventh day after a new store goes live, you receive an association risk alert, or customer service processes a refund for Store A in Store B—both things look like 'too many stores,' but they are actually not the same thing. For multi-store account management, there are really only three things you need to configure: an independent login environment for each store, sub-account permissions divided by role, and traceable operation logs. These three blocks depend on each other; if one is missing, the other two will fail.
First determine which layer the problem is in, then configure block by block; this can save a lot of rework.
First distinguish: are you dealing with an association risk control issue or a team collaboration issue
Platform-side signalsPoint to overlapping environments and credentials: two-factor verification starts triggering frequently, you receive alerts about multiple accounts or associations, products are delisted in batches, and withdrawals are delayed for review. The direction for handling these signals is to upgrade isolation, not to change passwords—changing passwords does not change the egress IP or browser fingerprint.
Team-side signalsPoint to missing permissions and logs: the same order has been replied to by two customer service agents, a price change was made in the neighboring store, an account is still usable after an employee leaves, and after finance exports data, it is impossible to find out who performed the operation. For these problems, first define roles and fields; the tool is only the carrier.
当两种信号同时出现时,先处理平台侧。协作层可以用制度临时兜住,环境层一旦被判定重合,补救成本高得多。
登录环境隔离:需要隔开的不只是 IP
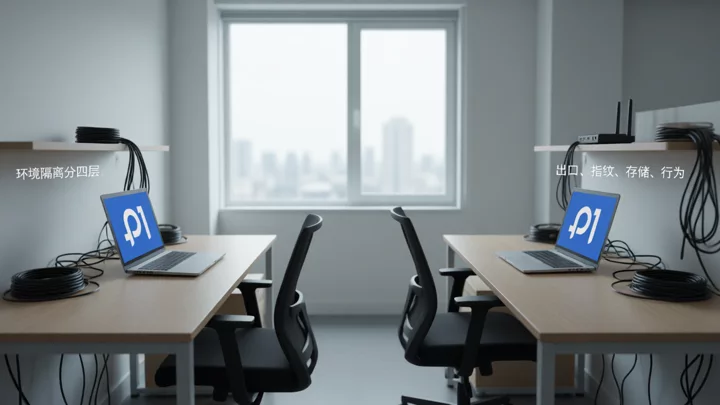
平台看的是重合度,不是单个信号。下面四层里任何两层重合度高,都可能被归到同一运营主体,具体处置以账户通知和平台官方政策为准。
- 出口 IP 与网络: 每个店铺固定一个独立出口,最忌所有店铺共用同一个代理。同一出口下同时登录两个店铺,是最常被记录的重合点。出口地区最好与账号注册主体、收款地区对得上。
- 浏览器指纹: User-Agent、时区、语言、分辨率、Canvas/WebGL、字体列表。同一台电脑用同一个浏览器开两个店铺,这组参数一模一样。
- Cookie 与本地存储: 退出登录再登另一个账号,Cookie 和 localStorage 经常清不干净,历史站点数据仍然能对上。
- 设备与行为痕迹: 同一设备标识、高度一致的操作时间规律、同一个收款账户、同一个退货地址、同一套客服话术模板。
最常见的四个错误:只换 IP 不换浏览器环境;多个店铺挂同一个代理出口;在同一个浏览器里切换账号;用同一个手机号或邮箱收验证码。浏览器多配置文件是成本最低的做法,但命名要有规范(店铺代码-平台-环境编号),否则两三个人用几天就分不清哪个环境对应哪个店。
Sub-account setup: split permissions by role, not by store.
Distributing passwords by store is the easiest approach, and also the root cause of permission chaos: one person handling customer service for three stores has three sets of account passwords, and when personnel change, all of them need to be reset. The correct approach is to split permissions into two layers—The role determines what actions can be performed; the store determines what data can be viewed.故答案为:.
| Position | Can view | Can edit | Requires secondary confirmation |
|---|---|---|---|
| Operations Supervisor | Order, inventory, and advertising data for all stores | Change prices, list/delist products, and adjust inventory thresholds | Bulk price changes, bulk delisting |
| Customer service | Orders and after-sales conversations for assigned stores | Refunds, address changes, and issuing replacements | Refunds over threshold, modifying recipient information |
| Procurement and logistics | Inventory, purchase orders, tracking numbers | Create purchase orders, update logistics information | Modify logistics for shipped orders |
| Finance | Settlements, bills, withdrawal records | Reconciliation flag | Withdrawal, binding a new payout account |
A few hard boundaries that must be firmly locked down: do not let operations staff concurrently hold permissions for withdrawals and payout account binding; batch price changes, batch delistings, and excess refunds must all go through secondary confirmation; exporting customer information should be opened only to roles that genuinely need it. Also add a handover status field (Pending / In Progress / Handed Over), which can directly eliminate the situation where two customer service reps reply to the same ticket.
Operation logs: what to record, who reviews them
The value of logs lies not in full-volume recording, but in pinpointing the person and time within five minutes when something goes wrong. Fields must cover at least these categories:
- Login records: account, time, egress IP, device or environment identifier
- Price changes and inventory changes: value before change, value after change, operator
- Data export: which fields were exported, how many records, and which account was used
- Permission changes: who granted what permission to whom, and when it was revoked
- Fund operations: refunds, withdrawals, binding or changing payout accounts
The retention period should cover at least one full reconciliation cycle; for operations involving funds and customer data, 12 months is recommended. The reviewer should not be someone from the position being audited; for small teams, having the store manager look at the exception list once a week is enough — there is no need for a full review.
Configuration order for the three things: environment → permissions → logs
- First, lock down an independent login environment for each store, create records following the naming convention, and confirm one by one that the outbound IP is not shared with other stores.
- Then set up four basic roles by position, assign people to roles, confirm that no one shares the same account and password, and revoke access immediately upon departure.
- Then enable logging, manually perform one price change, one export, and one permission change, and verify one by one whether each was recorded and whether the fields are complete.
- Finally, set exception rules and a review cadence: who reviews, how often, and what process to follow when an exception is found.
The order cannot be reversed. If you build logs first and add the environment later, the environment identifier field will be missing, which amounts to starting over; if you split permissions first and then define the environment, the account system will have to be changed again.
When you need dedicated tools and when a spreadsheet is enough
With 3 stores or fewer, a single platform, and 2 to 3 people, multiple browser profiles plus one permission ledger, together with the platform's built-in sub-account feature, is usually enough. With 5 stores or more, or when operating two or more platforms at the same time, manual maintenance of environment isolation is prone to errors, so an anti-association browser or a unified store management tool only becomes worthwhile then. When the team exceeds 5 people and customer service requires shift scheduling, permissions and logs must be handled by a system — a spreadsheet cannot keep up with these high-frequency changes.
The deciding signal is not the number of stores itself, but whether you have already experienced environment mixing or whether anyone has shared an account. Once you reach that point, compare tools by layering data permissions and login environments,Comparison of Multi-Store Management Tools for Cross-Border E-Commercein which a capability boundary comparison is provided; if the problem lies in fund pooling and inspection cadence,Multi-store management SOP from account isolation to fund pooling can be followed directly. TikTok Shop sellers can also first use Environment troubleshooting and risk self-check for TikTok Shop multi-store operationsRun through the four-step self-check, and for issues at the team collaboration level, refer to Team collaboration processes and permission settings in Shopify store management. For platform-level quantity constraints and compliance points, see Platform risk control rules and compliance points for cross-border e-commerce multi-store operations.
Frequently Asked Questions
Can you log into two stores in the same browser just by clearing browser cookies?
It cannot be the only method. Cookies are only one of four layers of signals; browser fingerprints, egress IP, and device identifiers will not change just because you clear storage. To do it really cleanly, use separate browser profiles or separate environments.
Can financial permissions be assigned to the store manager as an additional role?
We don't recommend granting them by default. If the store manager also handles withdrawals and binds the receiving account, that puts operational control and the outflow of funds in the same account, and the logs lose their cross-verification value. If it's truly necessary, grant one-time authorization and revoke it once the task is done.
How long should operation logs be retained?
At least cover one complete reconciliation cycle. Records involving refunds, withdrawals, and customer data exports should be kept for 12 months; for the rest, the default retention period in the platform backend is sufficient.
Does a small team of three or fewer people also need separate sub-accounts?
Yes, but it can be simplified into two roles: an operations role that can change prices and inventory, and a customer service role that can only handle orders and after-sales. The biggest risk of sharing an account isn't efficiency, it's being unable to pinpoint the problem when something goes wrong.