


Logging in to five stores separately works fine, but once the same operator handles orders, price changes, and customer service at the same time, CAPTCHAs begin appearing frequently, and the ERP shows records of the wrong store being modified or inventory being written to another site. Most teams' first reaction is to switch browsers or ERPs, but the problem is often not the number of stores; rather, it is that the four layers are not consistently mapped: account entity, seller center role, login environment, and tool write access.
The account structures of Temu, AliExpress, Shopee, Lazada, and Mercado Libre are not interchangeable, so directly applying one set of 'multi-account' experience will inevitably miss items. Below, we first look at platform differences, then at tool write boundaries, and finally provide a practical troubleshooting sequence; for more detailed fault breakdowns across the five platforms, refer to.Seller tool selection and store management troubleshooting for multi-account operations on Temu, AliExpress, Shopee, Lazada, and Mercado Libre
Problems only arise when multiple stores are operated together: first fix the four-layer mapping
The so-called four layers break down how a store operates into four things that must correspond one-to-one: which business entity opened the store, what roles and sub-accounts this entity has in the seller center, who operates in what login environment, and which tool writes data to the store with what authorization scope. When logging in separately, the four layers happen not to be triggered at the same time, so everything appears normal.
Once the team processes orders in parallel, all four layers are invoked at the same time: the same operator clicks buttons across multiple stores, the same ERP uses the same token to cover multiple stores, and the same browser environment contains both a main account and sub-accounts. At this point, whichever layer lacks a fixed mapping is where the problem emerges—manifesting as CAPTCHAs, permission crossover, or writing to the wrong store, rather than as a functional defect of a single platform.
Account Structure and Backend Role Differences Across Five Platforms
The table below compares only the aspects that affect tool integration and does not cover the registration process. Specific role names, sub-account granularity, and multi-store rules are subject to what is currently displayed in each platform's seller center.
| Platform | Account Entity and Multi-Store Scope | Seller Center Roles/Sub-Accounts | Common Risks of Tool Writes |
|---|---|---|---|
| Temu | Onboarded as a business entity; fully managed and semi-managed stores follow different operational paths in the backend | Operations are mostly performed through the main account, with limited roles available for assignment | The same operator handles both store types in succession, mixing stocking orders and orders in writes |
| AliExpress | Verified as a company or individual entity; one entity may operate multiple stores and must comply with the platform's multi-store rules | Seller Center supports sub-accounts and module-level permission assignment | Sub-account permissions are granted too broadly and not revoked for a long time, allowing customer service agents to change prices beyond their authority |
| Shopee | Multiple stores are linked under the main account, with permissions granted separately by store | Main account + sub-accounts; sub-accounts are bound by store | Multiple people share the main account login environment, and cross-store authorization for sub-accounts leads to changes in the wrong store |
| Lazada | Seller Center is managed by store; cross-border stores and local stores have different backend entry points | Sub-accounts are authorized by store and functional module | A single ERP authorization covers all stores, with a write scope exceeding job responsibilities |
| Mercado Libre | Operated by site (country), with a one-to-one correspondence between accounts and sites | The admin backend is organized by account; multiple sites must be accessed separately | Multiple sites share one login environment and ERP mapping, so prices and inventory can be written to the wrong site |
The most easily overlooked column in the table is the third column. Most teams only check 'who can log in' and not 'who can write what.' Temu and Shopee differ considerably in account setup details; for further reading, seeTemu and Shopee Seller Account Setup Guide; Standalone stores such as Shopify, by contrast, revolve around store owner accounts and staff permissions, which follow a different logic from marketplace stores; for comparison, see Shopify Official Help Center's staff permissions documentation. For eBay seller rules and store operations entry, see eBay Seller Center.
Tool Write Boundaries: Where ERP and Customer Service Tools Are Most Prone to Errors
To apply these differences to tools, you only need to focus on four things:
- Authorization granularity:能否只授权单个店铺、单个模块。授权到“全部店铺”最省事,也最容易串店。
- Write scope:订单、改价、库存、客服回复是否可分开授权。客服岗位通常不需要改价权限。
- Credential lifecycle:令牌何时过期、人员离职后如何回收。授权残留是权限串用的常见来源。
- Operation concurrency:同一操作人在同一时间对不同店铺执行写操作,是验证码与写错店同时出现的高发场景。
这四项里,指纹浏览器只负责登录环境这一层,ERP 负责业务写入这一层,两者不能互相替代。用指纹浏览器分环境但共用一个 ERP 操作人,串店风险依然存在;反过来,ERP 权限分得再细,多个店铺挤在同一个登录环境里照样会触发验证。
Four-layer mapping diagram: account principal—backend role—login environment—tool write access
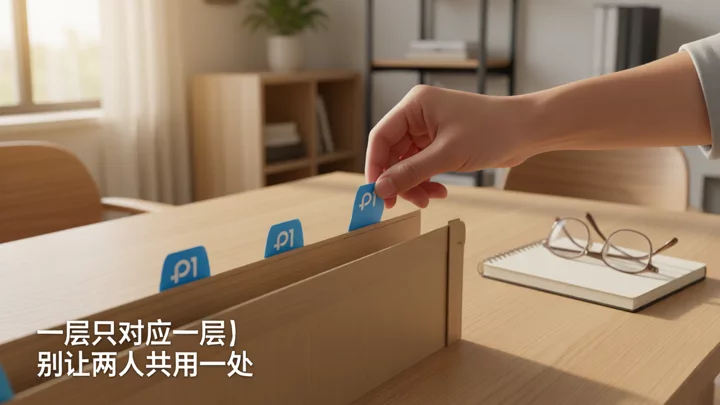
四层里最容易断的是两个节点。第一个是同一操作人跨多店处理订单:人只有一双眼睛,但后台会同时收到多个店铺的写请求,登录环境层和角色层的对应关系在这一刻被打乱。第二个是 ERP 授权范围大于岗位职责:一个客服账号拿着可改价的令牌,出问题时无法从日志判断是有意操作还是误点。
The fixed mapping approach is simple: each store occupies one row in the table, clearly listing the entity, the primary account owner, available sub-accounts, the bound login environment, and the ERP-authorized store ID. This table does not require tool support, but it must actually be completed and updated as personnel change; otherwise, troubleshooting can only rely on guesswork.
How to choose a store management tool: five check items are more useful than a feature list
The longer the feature list, the harder it is to judge. Use the following five acceptance checks; if any one fails, do not go live yet:
- Fixed correspondence between environments and accounts: A store can log in only within one environment, and the environment cannot be opened by two people at the same time.
- Proxy egress can be locked: After an egress is bound to a store, it can be queried, modified, and logged, rather than being randomly assigned.
- Permissions can be delegated and revoked: Role permissions can be narrowed down to a single store and a single module; when an employee leaves or changes roles, they can be revoked with one click and an audit trail is retained.
- Write scope can be limited: Orders, price changes, inventory, and customer service can be authorized separately; unauthorized operations are directly rejected rather than discovered after the fact.
- Logs can reconstruct a single action: it can identify who, in which environment, through which token, made a price change or reply to which store.
For the mapping between these five items and Seller Central role permissions, refer toHow to Manage Seller Central and Store Management Tools in Amazon Multi-Account Operationsfor the selection and troubleshooting checklist; for the boundary between tool capabilities and compliance responsibilities, seeIs it safe to use a fingerprint browser for multi-account operations? . When the store matrix the team needs to manage goes beyond the browser layer, you can alsoMulti-Account Management Solutionsto learn the basic breakdown of environments, roles, and devices.
Troubleshooting Sequence for Frequent CAPTCHAs and ERP Writing to the Wrong Store
If you get the order wrong, you will waste time switching tools. Follow the five steps below, and require evidence at each step before moving on:
- First, stop concurrent operations.Have the same operator pause cross-store order processing and price changes, and keep only one action per store. If CAPTCHAs drop immediately, the problem lies in the relationship between environment and concurrency, not in the tool itself.
- Check the mapping between accounts and login environments.Compare the store mapping table line by line to confirm that no two stores share one environment and no one is logged in to multiple main accounts at the same time.
- Check roles and permissions in Seller Center.Confirm that sub-account permissions match job roles, especially checking whether anyone holds both price-change and customer service permissions at the same time and whether accounts of departed employees remain.
- Check ERP tokens and store authorizations.See which stores the token covers, how long it is valid, and whether it matches the current role; if the authorization scope exceeds the responsibilities, narrow it first and then observe.
- Review store mappings and operation logs.Locate the action that wrote to the wrong store and confirm whether it was a mapping misconfiguration (wrong store ID bound) or the operator selecting the wrong store. In the former case, change the configuration; in the latter, revoke permissions.
Only if there is still no improvement after all five steps have been completed should you replace the browser environment or switch ERP. Directly changing tools often carries the old problems over to the new tool unchanged.
Troubleshooting sequence diagram: rule out issues layer by layer from the login environment to tool writes
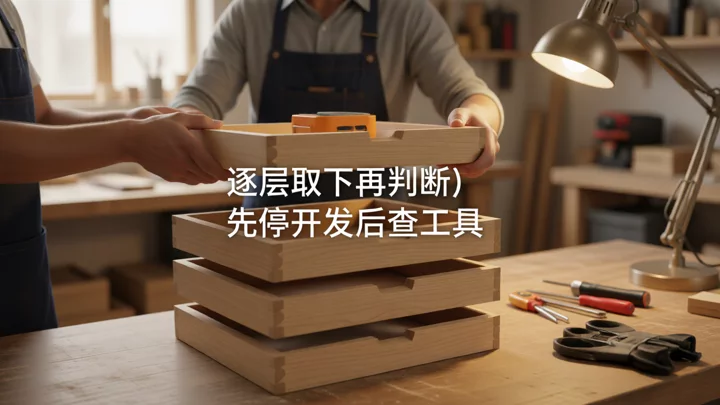
The left half of the diagram shows the login environment and CAPTCHA signals, while the right half shows tool writes and store-crossover signals. The two lines converge at the first step, because concurrent operations can cause both types of symptoms to appear at the same time; the hierarchy cannot be inferred backward from symptoms alone and can only be ruled out sequentially.
Multi-account compliance boundaries: five platforms cannot share one set of unlimited expansion logic
The premise of multi-account operations is legitimate business needs and entity compliance. Take Amazon as an example,Official guidanceIt mentions that typically one account is operated per region, multiple accounts may be allowed when there is a legitimate business need, and a policy issue with one account may affect related accounts. Other platforms have different rule interpretations, so official policies need to be checked one by one.
What tools can do is fix the correspondence among entities, environments, roles, and write scopes, reducing the probability of environment crossover and mistaken writes; they cannot replace the compliance qualifications of the account entity, nor guarantee that platform risk controls will not be triggered. When enforcement occurs, rely on account notifications and official policies, and simultaneously investigate multiple possible signals such as login environment, proxy egress, and operator; do not attribute it to a single factor.
Frequently asked questions
Can the same set of ERP accounts be bound to all stores on five platforms?
Technically, this can often be bound, but it is not recommended from a management perspective. Once the authorization scope covers all stores, any mistaken store selection will result in a cross-store incident, and logs will make it difficult to distinguish responsibility. A safer approach is to split ERP operators and authorization scopes by platform or by role, so that one account only touches stores within its responsibilities.
What should be noted about tool authorization for Temu fully managed and semi-managed stores?
The two types of stores have different backend operation paths and document types; mixing them under the same operator and the same environment makes document entry errors most likely. It is recommended to assign different operators by store type and mark the type separately in the mapping table, rather than writing only the store name.
How should Shopee main accounts and sub-accounts be divided to prevent customer service from modifying the wrong store?
The main account is used only for authorization and personnel management and does not participate in daily order processing; customer service sub-accounts are bound separately by store, with no cross-store permissions and no price modification module. This way, even if customer service selects the wrong tab, they cannot write to another store.
For Mercado Libre multi-site operations, should a separate login environment be prepared for each site?
When sites correspond one-to-one with accounts, environments should also be fixed by account rather than by person. If one operator manages three sites, they should use three account-bound environments to log in one by one, avoiding switching between multiple accounts in the same environment.
After a verification code appears, should you change the browser first or check the account entity and role permissions first?
First stop concurrent operations, then verify the mapping between accounts and environments, the role permissions in the seller center, and the scope of ERP authorization. If the account entity is non-compliant or role permissions are too broad, changing the browser will not help; after confirming that the first three layers are correct, then consider adjusting the environment or tools.

