

When multi-store logins are flagged as linked, the trigger is rarely the number of stores itself
What platform risk control records is the overlap in environment and profile left behind when multiple backends log in, not how many stores you have opened. Logging in to different backends repeatedly from the same computer, the same network egress, and the same browser configuration—these traces will be compared together; the difficulty of multi-store management is also rarely in opening the stores themselves, but in which set of login resources is used when opening them.
So the order should be: first confirm which layer you are stuck at, then build isolation by layer, and finally clearly define what can continue to be centrally managed. The following proceeds as “identify the layer → build isolation → define shared boundaries → set handover rules,” with judgment criteria at each step and no conceptual padding.
Four types of link triggers: first confirm which layer you are stuck at
Opening multiple stores itself is not the problem; the problem is that multiple cross-border e-commerce stores share resources on the same layer. Break “linking” into four layers, and you can pinpoint it by matching the signals:
| Layer | Typical signal hit | Can it be shared with other stores? |
|---|---|---|
| Login credential layer | Multiple backends share the same recovery email, phone number, or authenticator; frequent re-verification requests and backends being kicked offline | No. Recovery methods and two-factor authentication must be one set per store |
| Network egress layer | Multiple stores log in from the same IP or same proxy egress; CAPTCHAs are triggered collectively, and the login location clearly does not match the store's registration and operating locations | No. One long-term fixed egress per store |
| Browser environment layer | Cookie, local storage, UA, time zone, resolution, fonts, and other parameters overlap between two stores; human verification is required immediately after login | No. One independent environment per store with fixed parameters |
| Profile and behavior layer | Payment accounts, return addresses, customer service contact details, listing cadence, and creative assets overlap heavily; receiving an association alert or entering review | Some parts can be centrally managed, but externally visible fields must be kept separate |
If the issues are concentrated around “constantly being asked for verification codes,” check the network egress first; if they are concentrated around “backend disconnections and repeated re-logins,” check credentials and environments first; if warnings appear first and review follows, it most likely lies in the data layer. For a more detailed troubleshooting sequence, refer toBrowser Isolation and Network Environment Troubleshooting for E-commerce Multi-Account Management.
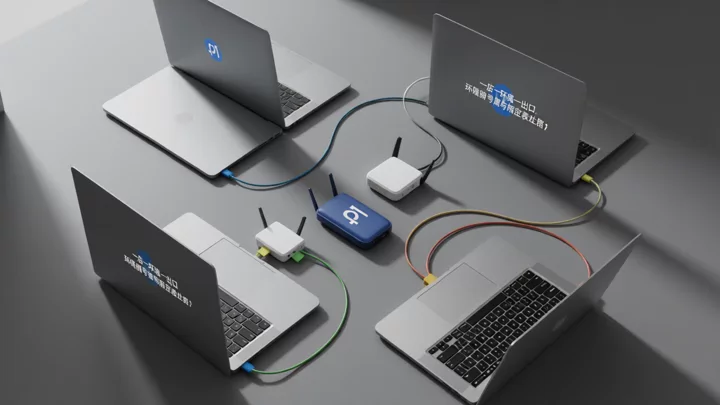
Four-step sequence for building an isolation solution: binding table → egress → environment → permissions
- Build the account binding table first, and only then touch any configuration.Fields should at least include: platform, store name, registration entity, login email, recovery phone, two-factor authentication device, egress number, browser environment number, person in charge, and receiving account. The criterion is that any store can be traced to a unique set of login resources, with no two stores pointing to the same environment number. If you start configuring environments before this table is properly built, once the stores grow in number, you will never be able to trace them back.
- Assign a fixed network egress to each store.The egress region should be roughly consistent with the store's registration location and operating location; once configured, it should remain unchanged long term, and multiple stores should not share the same one. The criterion is that no one on the team needs to temporarily disable the proxy in order to log in.
- One browser environment per store.Within an environment, parameters such as UA, time zone, language, resolution, and fonts are fixed, and the login state and local storage belong only to this one store. The criterion is that when two stores are open at the same time, they cannot see each other's Cookies. When choosing a multi-store operations tool, focus on just two points: whether the environment can be saved stably and whether the proxy can be bound directly to the environment. This is also the most fundamental difference between a store management tool and an ordinary cross-border e-commerce operations tool. For specific configuration, seeFingerprint Browser Environment Isolation and Proxy Configuration.
- Finally, lock down permissions.Assign operational permissions by store. Customer service and operations staff enter only the environments they are responsible for, do not share the main account password, and every login action is traced to a specific person.
This sequence has different emphases on different platforms: Amazon looks at the entity and export boundary, Shopify uses independent stores as the unit, and TikTok Shop also ties stores and advertising assets together. The baseline versions are inPractical Guide to Anti-Association in Cross-Border E-Commerce Multi-Store Operationswhere they are listed separately by platform.
What Must Be Completely Isolated and What Can Continue to Be Shared
Cutting everything apart is another kind of waste: operational data that is invisible at the login layer does not need another workflow created just for 'isolation'.
- Must be one set per store:Login email and recovery phone, two-factor authentication devices, network egress, browser environment and local storage, and payment collection and contact details visible to the platform. These five items are directly compared when determining association.
- Can be centrally managed:ERP order and inventory definitions, financial reconciliation, customer service script library, creative asset and product selection library. These are internal data and do not enter login-layer comparison; centralized management actually reduces errors.
- Intermediate items that require separate judgment:Registration under the same entity, shared payment collection, and shared return address. These are platform-level visible information that browser isolation cannot isolate; they are business decisions and are separate from login isolation. For how to divide permissions by platform, refer toComparison of Permission Schemes for Shopify Multi-Store and Amazon Multi-Account Management.
For the specific isolation items for Amazon multi-store, you can followAmazon Multi-Store Anti-Association Checklistto check them one by one, focusing on whether the egress and payment collection are reused.
The three steps where multi-person collaboration is most likely to break down
- Sharing login credentials.When operators borrow each other's main account to “take a quick look,” a single borrow merges the login records of two stores. Switch to assigning sub-permissions by store: everyone can view, but only the stores they are responsible for.
- Verbal environment handover.When someone takes over, they only mention the store name, not the environment number and exit number, and the new person casually logs in with the default environment. Handovers must clearly state the environment number, exit number, current login email, and verification method.
- Temporary shift coverage by a substitute.During major promotions, logging into the backend from a personal computer and home network is where isolation setups are most often breached. Better to leave a shift empty than to log in from an uncontrolled environment.
What these three steps have in common is that they pull an already-built isolation setup back into a shared state.The collaboration dimension when teams choose a fingerprint browserThe permission granularity, environment handover, and operation logs mentioned in it are precisely intended for these three steps.
Frequently Asked Questions
Can one computer log in to multiple stores at the same time?
It depends on whether they are in mutually isolated environments. Switching between multiple backends in the same browser window and under the same exit is the way most likely to result in overlapping records; if each store has its own independent environment and a fixed exit, the login action itself does not constitute a basis for determination.
If there are only two or three stores, do we still need full isolation?
No need for the full set. The binding table and independent exit are the two lowest-cost and most directly beneficial steps, so do them first; environment isolation can be completed later when the number of stores increases or after abnormal signals have already appeared.
For multiple stores registered under the same entity, does isolation still make sense?
Yes, but the scope covered is different. Entity information is visible at the platform level, and browser isolation cannot cover it; what can be controlled is login credentials, exits, environments, and operational traces. Whether to separate by entity is a business decision and should be evaluated separately from login isolation.
If multiple stores have already been logged in through the same exit, can it still be used?
If CAPTCHAs, logouts, or warnings have occurred, it is advisable to split each store onto its own long-term fixed exit rather than continuing to add stores to the same exit. Even when there are no anomaly records, you should also take the opportunity to split them apart during the next adjustment.
What should be noted during handover when an employee leaves?
Change the store's login password, recovery email, and two-factor authentication device, while confirming that the environment ID and exit ID remain unchanged. These two items must be written into the handover checklist to prevent the person taking over from rebuilding the environment.