


Logging into three Amazon stores separately works fine, but once they are connected to the same ERP, CAPTCHAs start popping up frequently, orders are written to the neighboring marketplace, and a colleague who left two months ago can still access the backend to change prices. Most people’s first reaction is to switch tools or check browser fingerprints, but a more common cause lies elsewhere: the four layers of account entities, Seller Central roles, login environments, and tool write scopes do not have a fixed one-to-one correspondence.
Let's start with the conclusion. Amazon Seller Central is the backend that determines “who can enter, what they can view, and which step they can take,” while store management tools are the external execution layer that determines “what to change in bulk and which store to apply it to.” The compliance boundary is essentially drawn between these two statements: once the correspondence is fixed, tools are eligible for integration.
First, align on terminology: what do multi-account, multi-store, multi-employee, and multi-platform each refer to?
These four terms are often used interchangeably, yet their risk points are completely different. Breaking them down first ensures that subsequent discussions on compliance and tool integration remain clear and consistent.
| Term | What it actually refers to | Where the risk lies |
|---|---|---|
| Amazon multiple sales accounts | Multiple seller accounts operated by the same or different entities under legitimate business needs | Account entity and account health; policy issues with one account may affect other accounts |
| Multiple sites/stores under the same account | Sites such as North America, Europe, and Japan enabled under a single seller account | Seller Central roles and site authorization scope |
| Seller Central sub-accounts | Functional permissions for employees logging into the same account using their personal identities | Roles and permissions, not account quantity |
| Cross-platform stores | Independent backends on platforms such as TikTok Shop, Shopify, eBay, and Shopee | Write scope of the login environment and tools |
The most problematic misnomer is labeling 'three employees logging into the same store' as 'multi-account operations.' It is actually just a permissions management issue, which can be resolved using sub-accounts and roles, without requiring additional entity or environment isolation.
The five entries sellers actually use daily in Seller Central
Seller Central has many features, but those directly related to account governance and daily operations are concentrated in these areas; others can be explored as needed:
- Account Health: Check performance metrics, policy alerts, and appeal progress. This is the entry point for determining whether the account can continue to operate normally.
- User Permissions Management: The primary account holder adds employees, assigns permissions, and deactivates departed staff here. This is the source of the sub-account system.
- Orders and Inventory: Daily fulfillment and maintaining available quantities. These are also the two data areas most frequently written to by tools.
- Business Reports: Sales, traffic, and inventory reports. These serve as the reconciliation baseline for finance and operations.
- Performance Notifications and Cases: policy changes, audit notices, and issue tickets—often the answer to why you suddenly lost permissions.
The purpose of these five entry points is to establish a factual foundation: who is in the account, whether the account is currently healthy, and where the data baseline comes from. Skipping this step and going straight to tools is like asking external systems to guess your permission structure.
Compliance boundaries for multi-account operations: what is officially allowed is legitimate business need, not evasion of review
Boundaries must be understood according to official guidelines. Amazon's official guidance on multiple seller accountsstates that typically one account is operated per region, multiple accounts are permitted when there is a reasonable business need, accounts should be maintained in good standing, and policy issues with one account may affect related accounts.
From this, two sides can be drawn. The compliant side is: having a genuine business reason (different brands, different category lines, different entities, or operating in different regions), with each account corresponding to a clear entity and payment relationship, and maintaining account health individually. The non-compliant side is: batch-opening stores with false entities, switching identities via shared login credentials, or splitting accounts for the purpose of evading review or association.
It should be noted that the platform's disposition of accounts often references multiple signals simultaneously, and the official criteria for specific judgments have not been publicly disclosed. Therefore, do not believe claims that "a single specific action inevitably leads to association." When encountering permission or audit issues, rely on account notifications and official policies, and then re-verify your entity and permission relationships.
Four-layer mapping: aligning account entity, Seller Central roles, login environment, and tool write scope
This relationship diagram is worth posting on your operations workstation. Each layer answers only one question; if any layer is misaligned, it will manifest elsewhere as 'the tool is not working well.'
Layer one is the account owner: which company or individual owns the store, and which payment account and tax file it corresponds to. Layer two is the seller center roles: which employees are accessing the platform, in what capacity, and which marketplaces and modules they can view. Layer three is the login environment: who is operating on which device and over what network, and whether credentials are shared across multiple people. Layer four is the write scope for tools: which fields and which stores your ERP or store management tools are authorized to update.
The consequences of misalignment are easy to spot: when the owner and store are mixed up, a single incident can affect multiple stores; when roles are undefined, employees end up sharing a single main account; when environments are mixed, verification codes and two-factor authentication prompts keep showing up; and when write scope is not limited, price and inventory changes can leak into the wrong stores.
Before connecting a store management tool, first validate the four boundaries for writing
Having many features does not mean it is safe to centralize management. We recommend locking in this sequence of four steps before scaling to a second batch of stores:
- Store Binding and Entity Mapping: For each store bound, register which entity, site, and receiving account it corresponds to. The binding list must be cross-referenceable one-to-one with the account list in the Seller Central.
- Read-Write Permission Levels: Start by enabling read-only access, allowing the tool to pull and verify complete data for orders, inventory, and reports. After confirming the data source is accurate, gradually open write permissions item by item.
- Field-Level Write Scope: Clarify which fields can be written in bulk and to which stores. For instance, if the same SKU has inherently different prices across sites, price authorization must be granted separately per site; inventory writes are restricted to the primary store, with other stores updated via synchronization rules rather than direct modification; order status write-backs are limited to the fulfillment scope.
- Operation Logs and Read-Back Validation: Every bulk action must have a traceable record. After execution, verify the results by reading back from the front end or Seller Central, rather than relying solely on the tool's "success" prompt.
Acceptance criteria can be simple: randomly sample ten price or inventory modification records, and verify each one individually in the corresponding store backend. If even one record was applied to the wrong store or site, immediately suspend bulk write permissions for that field, rather than continuing to expand the integration scope.
Configuring Employee Permissions: One-to-One Mapping Between Seller Central Sub-Accounts and Tool Roles
The challenge in permission configuration is not technical, but requires simultaneous constraints on roles, stores, and actions. The following table can serve as a starting template, to be adjusted based on actual business needs:
| Role | The Seller Central side | Role within the tool | Common mismatches |
|---|---|---|---|
| Entity responsible party | Primary account holder; payment and tax information is visible to them only | System administrator | Treats the primary account as an everyday operational login, accessible to everyone |
| Operations | Product, pricing, and order authorization on a site-by-site basis | Store-level operations role with authorized permissions | One-time authorization across all stores, allowing price changes without site restrictions |
| Customer service | Order viewing, buyer messages | Orders and messages only, no prices or inventory | Borrowing an operations account to reply to messages, incidentally exposing cost prices |
| Finance | Payment reports, settlement data | Read-only reports, no write access | Multiple users sharing the same login credentials |
| Warehousing & fulfillment | Inventory and shipping operations | Inventory writes restricted to the main warehouse store | Inventory sync rules write back to all sites |
Offboarding and revocation is the most commonly overlooked step. Three areas must be handled simultaneously: deactivating user permissions in Seller Central, deleting the account within the tool, and removing email addresses and two-factor authentication methods associated with the employee. Addressing only one side leaves a typical security risk where the person is gone but permissions remain active.
Write-Scope Acceptance Checklist: Verify item by item before going live
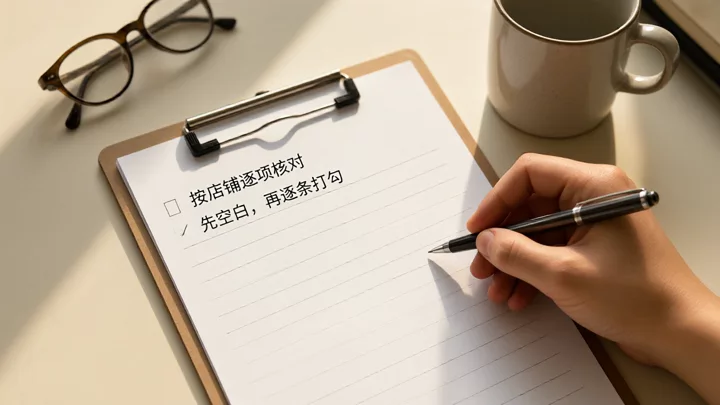
Turn the four steps above into a screenshot-ready checklist and verify it shop by shop during review, not by feature:
- Shop: Ensure the number of linked shops matches the seller center account list. Each shop must have a clearly defined legal entity and site.
- SKU: Check whether a mapping has been established for identical SKUs across shops. Unmapped SKUs are not allowed for bulk writes.
- Price: Grant authorizations separately for each site. Verify whether the price sources for multiple sites of the same SKU are unified.
- Inventory: Clearly identify the shop from which inventory is deducted. Cross-entity mutual writes are prohibited.
- Order: Status write-back scope is limited to fulfillment and does not include settlement data.
- Logs: Every bulk action must be traceable to a specific person, timestamp, shop, and field.
If only handling Amazon: Sort out permissions first, then consider the tool
If Amazon is the only platform you currently work with, the focus should be onIsolation Checklist for Amazon Multi-Account OperationsandThe sequence for permission configuration after seller account registration; wait until the second batch of stores appears, then addMethod for dividing roles among multi-store sub-accountsis more efficient than piling up tools from the start.
Minimum acceptance criteria before launch: five traceable points
No thick documentation is required; having these five records is sufficient to support subsequent troubleshooting and handover:
- Store-Entity List: Which business entity, site, and payment account corresponds to each store.
- Role Matrix: Position × Store × Executable Actions. Finalize these three columns before creating accounts.
- Screenshot of Tool Write Scope: Take one screenshot on the day of integration, and take another after any configuration changes.
- Operation Log Sampling: Randomly select ten batch actions and re-read the corresponding backend to confirm the implementation results.
- Offboarding recovery checklist: Seller Central disabled, tool account deleted, email and two-factor authentication unlinked. Three items checked off.
At this point, the division of roles between the Amazon seller account and the Seller Central is clear: Seller Central manages identity and permissions, while tools manage execution and scope. The compliance boundary for multi-account operations is not a vague line, but rather whether these four layers align.
Frequently Asked Questions
Under what circumstances are multiple Amazon seller accounts considered to have legitimate business needs?
The official stance is that 'typically one account per region, multiple accounts allowed if there are legitimate business needs,' but no exhaustive list is provided. Practically, two points can be observed: each account has an explainable operational reason (different brands, different product lines, different entities), and the entity, payment, and tax documents correspond one-to-one, with account health maintained separately for each. Splitting accounts to bypass audits or avoid association does not qualify as a legitimate business need.
Seller Central sub-accounts and ERP sub-accounts do not use the same set of passwords. How to thoroughly recover access after an employee leaves?
Handle it simultaneously in three places: Disable Seller Central user permissions, delete or downgrade the account within the ERP to read-only, and unlink the employee's bound email and two-factor authentication methods. It is recommended to include these three steps in the offboarding process and spot-check the operation logs after recovery to confirm that no residual scheduled tasks or API tokens are still writing data under that identity.
Store management tools can automatically adjust prices and sync inventory. Why do they still write to the wrong store?
In most cases, it is because field-level write scopes are not defined, rather than the tool itself making errors. The same SKU often has different prices across different sites, and inventory may also have distinctions between primary stores and synced stores. If batch writing is enabled solely based on 'store is linked,' the rules may fall back to incorrect default values and apply to other stores. The solution is to authorize by field and site separately, and to consistently perform post-execution read-back verification.
Just opened a second store. Should I buy ERP first or organize Seller Central permissions first?
Organize permissions first. Before the second store goes live, at minimum, you must determine entity ownership, who holds the master account, which roles need access, and how to differentiate login environments. If you integrate tools without these decisions, you will only concentrate and amplify originally scattered issues—verification codes, cross-store errors, and residual permissions typically appear simultaneously, and the troubleshooting cost is far higher than pre-configuration costs.

