

A new store is asked for video verification right after submitting information, an old store suddenly receives a linkage warning, and the backend is locked after an outsourced login is switched to another person—when the number of stores reaches the 2 to 10 range, these three types of failures occur most frequently. What is often shared is not the operating approach, but a specific resource at one layer: registration information, egress IP, browser environment, payment account, or login permissions. Below is a checkable checklist in the order of opening stores, including binding table fields, isolation configuration sequence, and inspection frequency. Its goal is to reduce the probability of environment crossover; it does not promise to bypass platform risk controls, nor does it replace genuine qualifications.
Build the Binding Table First: One Store, One Identity, One Environment, One Proxy—Then Discuss Store Count
The most common failure mode in expansion is opening stores first and then going back to add isolation. By then, the registration email, payment account, and login device have already been cross-used, leaving only after-the-fact separation, which is costly and prone to omissions. Before starting, fill in the table below completely; if any row is left blank, do not open a new store yet.
| Field | Content to Fill In | Cross-Use Red Line |
|---|---|---|
| Store Identifier | Platform + site + store backend ID | Two stores share the same login entry or recovery email |
| Business entity | Business license, legal representative, registered address | Multiple stores share the same legal representative without a reasonable business explanation |
| Collections and payments | Receiving account, charging credit card, tax information | Two stores are bound to the same card or the same receiving account number |
| Proxy IP | Exit region, static IP, provider, expiration date | Multiple stores share the same IP, or use frequently drifting dynamic IPs |
| Fingerprint environment | Environment ID, time zone, language, creation date | Multiple people each log in to the same store from their local browsers |
| Devices and owners | Device ID, primary owner, collaborators | No handover records, so there is no way to trace who has logged in to the environment |
The value of this table is that it turns isolation into something that can be checked. Once it is filled in, even newcomers can judge row by row whether this login falls on the correct environment and IP
Registration stage: Amazon multi-account qualification and materials isolation checklist
Amazon's stance on multiple accounts is conditional: usually one account per region, multiple accounts may be held when there is a legitimate business need, accounts must remain in good standing, and a policy issue with one account may affect related accountsAccount health guidance from Amazon's official seller forumIt is the first basis for determining whether you have a legitimate business need; do not let anecdotal experience replace it
- Business license and legal representative:One business entity, one set of materials; do not repeatedly register on the same site with the same license
- Email and phone:One set per store; the registration email must not be used as the recovery email for other stores.
- Registered address and business address:Keep it consistent with the license and payment collection information to avoid contradictions among the three addresses during review.
- Billing credit card:Use different cards for different stores as much as possible; at minimum, do not let the billing addresses completely overlap.
- Receiving account:One receiving account per store; avoid using the same account to receive payments for multiple stores.
- Tax information:Keep it consistent with the entity; do not use other people's information to fill out the form.
Environment and IP isolation configuration steps
After material isolation, the network and browser environment are the most likely to cause problems. Follow the order below; each step can be verified on the spot.
- Fixed proxy per store: the egress region matches the registered and operating locations, with one IP per store and no sharing across multiple stores.
- Create an independent fingerprint environment: one environment corresponds to one store; cookies, local storage, time zone, language, and resolution follow the proxy region settings.
- Bind devices and accounts: pin the environment to one device or one team account; members must not log in using their own local browsers.
- Verify before the first login: confirm that the egress IP's actual region, time zone, and DNS match the settings, then enter the account and password.
- Save environment snapshots: record the environment ID, proxy IP, and creation date; when handing over, transfer according to the record instead of giving verbal instructions.
Four practices to avoid: using dynamic IPs that drift frequently, multiple stores sharing one proxy, repeatedly switching nodes during login, and logging in to multiple stores on the same IP. The principles of environment isolation and selection criteria can be cross-referenced withHow to Choose and Use a Fingerprint BrowserandWhat Is a Fingerprint Browser, the former covers the configuration order, while the latter covers the isolation boundary.
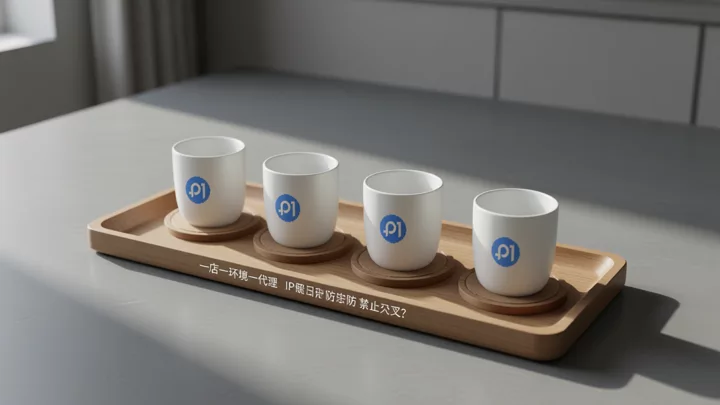
Binding relationship diagram: how stores, proxies, fingerprint environments, and devices align
The diagram below locks down the mapping among the four resources: a line connects only one object, and any crossing indicates a configuration error. It is also a pre-login check reference for customer service and outsourced staff—before opening the browser, first confirm that this line has not been merged with someone else's.
Daily anti-association checks: what to check daily, weekly, and monthly
Checks should be layered by frequency; otherwise, you will either repeat useless work every day, or only discover that no one has checked when a problem occurs.
| Frequency | Check item | Anomaly determination and handling |
|---|---|---|
| Daily | Whether the exit IP and region change, whether the environment is concurrently logged into by multiple people, account health notifications and verification prompts | If the IP is inconsistent with the binding table registration, stop operations immediately and switch back to the original node; for concurrent logins, freeze the environment first, then investigate. |
| Weekly | Browser version and plugin changes, whether new shared use has been added for payment collection and email, employee permission changes, proxy stability | Record the person making changes and the time; if new sharing is found, separate it within the same week. |
| Monthly | Review of entity information, proxy expiration and replacement records, consistency between the binding table and environment snapshots, and retrospective review of historical verifications or secondary reviews. | Inconsistent items must be corrected in the current month with records kept; do not let them accumulate across months. |
The value of inspection lies in clear thresholds. An IP anomaly is not a feeling; it is an inconsistency with the value registered in the binding table. A permission anomaly means someone outside the binding table can log in to that environment. If neither of these two conditions is met, no escalation is needed; if either is met, follow the anomaly process.
Inspection record sheet template: make checks traceable.
Checking without recording is equivalent to not checking. The record sheet should include at least eight columns: date, store, proxy IP and region, fingerprint environment ID, login user, anomaly symptom, handling action, and reviewer. A designated person reviews the consistency between the records and the binding table once a week, and writes discrepancies back into the table.
Team collaboration and the handling order after a trigger signal.
When a verification, secondary review, or association prompt appears, do three things first:Freeze the fingerprint environment and proxy corresponding to that store and stop logging in further; check whether the IP, payment collection, and information in the binding table overlap with other stores; archive that day's login records and page screenshots. Then submit materials according to the instructions in the account notification. Continuous logins and repeatedly switching nodes usually only expand the scope of investigation.
At the collaboration level, there are two hard rules: never share login credentials, and assign permissions by role. Customer service only needs order and message permissions, advertising only needs advertising asset permissions, and warehouse and finance staff do not access the store backend. On the day an employee leaves, revoke their environment access and update the owner field in the binding table—residual permissions are harder to detect than a leaked password.
FAQ
Can I log in to multiple Amazon stores from the same computer?
Technically yes, but opening multiple accounts in a regular browser shares Cookies, local storage, and device parameters, which easily causes environments to overlap. A workable approach is to give each store its own fingerprint environment and its own proxy, so logins fall on non-overlapping configurations. Whether accounts are deemed linked is determined by the platform based on a combination of multiple signals, not by a single factor.
Can one business license open multiple Amazon stores?
Amazon allows multiple accounts when there is a legitimate business need, but the accounts must remain in good standing, and a policy issue with one account may affect related accounts. Using the same license to repeatedly open stores on the same marketplace has limited justification; operating across marketplaces or through multiple entities is easier to explain. Ultimately, account notifications and official policies prevail.
How should I choose a proxy IP?
Prioritize IPs whose exit region matches the registration location and operating location, and that can be used as a long-term fixed IP—one dedicated line per store, not shared with other stores. Dynamic IPs and frequent node switching make the login environment appear unstable, while a shared IP directly places multiple stores on the same exit.
Can a fingerprint browser guarantee that accounts won't be linked and suspended?
No. What it isolates is the browser environment, reducing the overlap caused by shared Cookies, caches, and device parameters, but it cannot replace genuine qualifications, legitimate business conduct, and platform review. For identification mechanisms and compliance boundaries, refer toCan a fingerprint browser pass risk control?. Falsified documents, shared payment collection, and non-compliant operations will still trigger enforcement. For long-term management approaches for account matrices, seeKey Steps in Account Matrix Management.